N8 Review and Player Reputation
For a beginner, an N8 review should separate three questions that are often treated as one: what the platform presents itself as, what its retained research records report about its operating structure, and what those records can actually establish about player reputation. This distinction matters because a description of a website, a licensing reference, or a support channel is not the same as independent evidence of consistent player outcomes.
This article evaluates N8 using only the supplied research dossier. It does not present personal experience, a promotional description, or a legal ruling. The aim is to explain the evidence status in plain English and to show where the available material remains uncertain.

Research question and method
The research question is: what can the available evidence establish about N8 and its player reputation for readers in India?
The method is a narrow evidence review. The assessment considers five criteria:
- the platform identity and the services it is described as offering;
- the licensing and corporate information retained in the research notes;
- the Indian regulatory context recorded in those notes;
- the dispute-resolution route described in the platform terms; and
- the extent to which the records contain evidence about player reputation rather than only operator statements or technical descriptions.
Each point is kept at the strength used by the stored research. Where a record makes an attributed claim, this article identifies it as a claim in the research rather than adopting it as an independently verified conclusion. The review also avoids treating technical security controls as proof of licensing, fairness, legality, or satisfactory player treatment.
What the retained research describes N8 as offering
The stored research note on brand identity reports that N8 Casino operates primarily as a mobile-first online gambling platform targeting players in India. It describes a combination of sportsbook wagering, live dealer casino tables, and random-number-generator slots. This gives a broad picture of the product categories associated with the brand in the dossier.
That description is useful for defining the subject of the review, but it does not by itself answer whether the platform is legitimate, reliable, or well regarded by players. A product category is not evidence of an operator’s regulatory standing. Similarly, a listed service should not be read as proof that every game, table, or betting market is currently available to every visitor.
The evidence also does not supply a verified player-reputation dataset. The retained records do not establish a representative pattern of complaints, successful resolutions, satisfaction levels, or independent reviews that could support a general reputation rating. Individual statements, if found elsewhere, would still need separate assessment and could not automatically be extended to the whole player base.
Licensing: what the research says and what it does not prove
The licensing record states that N8 Casino operates within what the stored research calls an offshore grey-market legal framework. It reports that the platform has historically referenced authorisation under Curaçao eGaming master-licensing structures, specifically Antillephone N.V. licence number 8048/JAZ. The retained record describes https://n8bet-in.com as a mobile-first online gambling platform targeting players in India.
This wording must be read carefully. The record reports a historical licensing reference; it does not establish that the licence remains valid under the updated Curaçao framework. The preliminary research also identified the exact offshore licensing position as an information gap, including the question of whether a legacy master-licence claim corresponds to current validity under the Landsverordening op de kansspelen framework.
Accordingly, the available evidence does not justify stating that N8 holds a currently verified licence. It also does not justify stating that the Curaçao reference constitutes an Indian operator licence or approval. A foreign licensing reference and permission to operate in India are separate questions. The supplied records do not resolve that distinction for N8.
For a beginner reading an “Is N8 legit?” review, this is an important evidence lesson: the existence of a licence number in a website reference is not the same as a current verification of the licence, and neither point alone establishes an India-specific legal position.
Corporate identity and accountability
The corporate-structure record describes a dual-entity narrative that requires careful assessment. It reports that some regional landing portals and footer terms refer to management by the “N8 Group” or to offshore holding entities based in Curaçao.
This information indicates that the brand presentation may involve more than one named entity or regional web property. However, the record does not provide a complete, independently verified ownership chart. It does not establish which entity is ultimately responsible for every service, account, transaction, or dispute. The wording therefore remains descriptive and attributed to the stored research note.
For player reputation, corporate clarity matters because a reputation is easier to assess when the responsible legal entity, applicable terms, and complaint route are clear. In this case, the retained evidence describes the structure as requiring assessment but does not supply enough verified material to turn that observation into a conclusion about accountability or player treatment.
India-specific regulatory context
The regulatory record describes the legal landscape for online gambling in India as having undergone a structural shift following the enactment of the Promotion and Regulation of Online Gaming (PROG) Act, 2025, identified in the dossier as Act No. 32 of 2025.
This record provides context for why an N8 review aimed at readers in India should not rely only on an offshore licensing reference. It does not, however, supply the exact commencement date of the Act, a readable notification confirming every operational consequence, or an operator-specific determination concerning N8. The supplied evidence therefore does not establish N8’s legal status in India.
The correct interpretation is narrower: the research notes identify a significant Indian regulatory context that must be considered, while leaving the operator-specific position unresolved. Readers should not treat a sports-betting page, a gaming website, or a foreign licence reference as proof of an India-wide operator licence.
Dispute resolution and the meaning of support access
The retained policy record states that N8’s contract terms identify internal customer-support channels as the primary mechanism for player dispute resolution. It names 24/7 live chat, official email support, and official Telegram support handles as the channels described in those terms.
This is evidence about the stated process, not evidence that disputes are resolved successfully or independently. The record does not provide a measured response rate, an audited complaint outcome, or a verified pattern of player satisfaction. It also does not establish that an internal support route has the same independence as an external alternative-dispute-resolution body.
For reputation research, the distinction is central. A support channel may show that the terms describe a route for raising a problem, but it cannot be converted into a claim that players generally receive effective assistance. The supplied records do not establish that broader performance.
Technical signals and their limits
The technical research note reports that N8’s primary web domain and alternative mirror URLs use TLS 1.3 with 256-bit AES session encryption, with modern SSL certificates associated with Cloudflare Web Application Firewall infrastructure. It also reports that the native Android application is distributed as a direct Android Package file because of Google Play Store restrictions on real-money gambling applications in India.
These points describe technical and distribution arrangements reported in the stored research. Encryption can describe how a connection is protected in transit, but it does not prove that an operator is licensed, that games are fair, that disputes are resolved well, or that a player’s overall experience is satisfactory. Likewise, direct APK distribution describes an installation route; it is not, on its own, evidence of legitimacy or illegitimacy.
The dossier further reports that account security uses a dual-layer structure separating ordinary login passwords from transaction-authorisation controls. This is a description of account-control architecture. The supplied material does not provide an independent security audit or a player-outcome study, so the technical claim should not be expanded into a guarantee about account safety.
What can be said about player reputation?
The strongest evidence-based answer is limited. The supplied records describe N8’s product categories, historical licensing references, a corporate-structure issue for assessment, an Indian regulatory context, internal support channels, and selected technical controls. They do not establish a broad, independently verified player reputation.
That means this review cannot responsibly label N8 as widely trusted, widely criticised, safe, unsafe, legitimate, or illegitimate on the basis of the retained material alone. Those would be broader judgments than the evidence supports. The records also do not establish a consistent pattern of payment experiences, withdrawal outcomes, game fairness, or complaint resolution, and this article does not fill those gaps with assumptions.
A common misreading is to combine several limited signals into a single verdict. For example, a licence reference, encrypted connection, mobile application, and support channel may appear reassuring when listed together. Yet each concerns a different question. Licensing requires current verification; security requires more than a connection protocol; application distribution does not establish legal status; and support availability does not establish successful resolution.
Limits and uncertainty
This review is constrained by the supplied dossier and is not a fresh verification exercise. The research notes themselves identify licensing validity as an information gap. The material also describes corporate references that require assessment rather than resolving them. The regulatory record supplies context but does not provide an operator-specific legal determination.
The date attached to the stored research is August 4, 2026, and the notes report conditions affecting N8 in India at that point. Regulatory, domain, policy, technical, and support information can change. The article therefore treats those details as retained research observations, not permanent facts.
There is also a category limitation. Technical descriptions and contract language are not the same as independent evidence of player reputation. Without a representative and independently assessed body of player-outcome evidence, a general reputation score would be unsupported. The supplied records do not establish such a score.
Conclusion
The retained evidence presents N8 as a mobile-first gambling platform associated with sportsbook wagering, live casino tables, and RNG slots. It reports historical references to Curaçao licensing, describes a corporate structure requiring further assessment, records an important Indian regulatory context, and identifies internal support channels and technical controls.
However, the evidence status is uneven. Several points are attributed research descriptions rather than independently verified conclusions, and the central question of broad player reputation remains unresolved by the supplied records. The most accurate conclusion is therefore not a promotional endorsement or a negative verdict, but a distinction between what N8 is described as offering and what the available evidence has actually established about its licensing position, accountability, and player experience.
What method was used for this N8 review?
The review uses a narrow reading of the supplied research dossier. It compares platform identity, licensing references, corporate information, Indian regulatory context, dispute-resolution language, and technical descriptions while preserving the attributed wording and uncertainty of the stored records.
Does the research establish N8’s current licence status?
No. A retained research note reports a historical reference to Antillephone N.V. licence number 8048/JAZ, while the investigation plan identifies current validity under the updated Curaçao framework as an information gap. The supplied records do not establish a current licence verification.
Does the available evidence establish N8’s player reputation?
No. The records describe services, support channels, corporate references, regulation, and technical arrangements, but they do not establish a representative and independently verified pattern of player satisfaction, complaints, or dispute outcomes.
Does encrypted access prove that N8 is legitimate?
No. The stored technical note reports TLS 1.3 and 256-bit AES session encryption, but that describes connection security. It does not establish licensing, legal status, game fairness, or successful player-support outcomes.

Rabby Wallet and Layer 2 Optimization: Reducing Fees on Arbitrum, Optimism, and Base Through Smart Routing
A trader on Ethereum mainnet faces a familiar problem: a swap that costs $2 worth of tokens in liquidity loss and slippage also requires a $15 to $40 gas fee, depending on network congestion. The same transaction on Arbitrum or Optimism might cost cents, with gas burned at a fraction of mainnet's rate. But moving funds between layers introduces its own friction: bridge fees, liquidity constraints, and the mental overhead of tracking assets across multiple networks. A practical solution requires understanding not just that Layer 2 networks exist, but when and how to use them, which chains offer the best economics for specific transaction types, and how a multichain wallet handles the complexity without turning every interaction into a manual cross-chain negotiation.
Rabby Wallet operates across multiple EVM-compatible networks and provides tools designed to reduce this friction. Transaction simulation, automatic network detection, and built-in support for Arbitrum, Optimism, Base, and other Layer 2 chains let users see costs before committing and move assets more efficiently than they would by manually choosing routes. The wallet does not abstract away the underlying network choices—it makes them visible and legible. For users who understand the trade-offs, that transparency becomes a cost-reduction tool. For those who do not, it can simply clarify which networks are expensive and which are cheap.

Understanding Layer 2 fee structures and why they differ
Ethereum mainnet processes transactions through a global consensus mechanism in which every full node must validate and store every transaction. That security comes at a cost: gas fees reflect the computational and storage resources required. A simple token transfer on mainnet may consume 21,000 gas units, and with a base fee fluctuating between 20 and 100 gwei depending on congestion, users pay between $0.50 and $5 for a baseline transaction. Complex smart contract interactions—swaps, approvals, staking—easily exceed 100,000 or 200,000 gas units, multiplying costs accordingly.
Layer 2 networks operate differently. Arbitrum and Optimism, the largest optimistic rollup networks, bundle multiple user transactions together off-chain, then post a compact proof to mainnet. Instead of storing every transaction on mainnet, they store only a compressed batch and a state root. That compression reduces per-transaction cost dramatically. Arbitrum charges a base fee (typically 0.1 to 1 gwei) plus a small L1 fee that represents the cost of posting that transaction's share of a batch to mainnet. Optimism uses a similar model with its own fee calculation. Base, built on the Optimism stack, follows comparable economics but benefits from lower transaction volume and therefore often lower fees.
The practical difference is striking. A swap that costs 80 gwei × 150,000 gas = 12 million gwei (≈ $36) on mainnet might cost 0.5 gwei × 150,000 + 5,000 gwei for L1 posting ≈ 75,000 + 5,000 gwei (≈ $0.30) on Arbitrum. That is a 100× reduction. Polygon and BNB Smart Chain, which operate as separate consensus chains rather than rollups, have even lower fees because they use fewer validators and can tolerate higher throughput; a transaction there might cost a few cents in gas. The trade-off is that security assumes fewer validators and no settlement back to Ethereum for finality.
An EVM wallet like Rabby makes these differences visible by showing gas estimates for the currently selected network. When a user is about to approve a token for a DEX or execute a swap, the fee display immediately reveals whether they are on an expensive network. That awareness is the first step toward optimization: if a transaction costs $35 on mainnet but $0.40 on Arbitrum, the decision to bridge and transact on Arbitrum becomes rational for any transaction worth more than a few dollars.
Smart routing: When to bridge, when to swap in place
A naive approach to Layer 2 optimization assumes all activity should move to the cheapest network. But bridging itself has costs and delays. A canonical bridge from Ethereum to Arbitrum or Optimism typically requires a confirmation period (7 days for Optimism's standard bridge, instant for liquidity-based bridges like Stargate) and charges bridge fees. Moving $1,000 worth of ETH might cost $30 to $50 in bridge fees and time, making it worthwhile only if the savings from subsequent transactions exceed that cost. A single swap saved $30 in gas by moving to Arbitrum is break-even; ten swaps save $300, a clear win.
The decision depends on transaction frequency and size. A large trader executing 20 trades in a week benefits dramatically from staying on a Layer 2. A casual collector making three transactions a month may find the bridge cost unjustifiable. A DeFi wallet should present the cost of the bridge and the savings from staying on Layer 2, but the decision ultimately requires individual judgment about usage patterns.
Rabby's automatic network detection helps by detecting which chain a connected application or transaction is intended for, reducing the friction of manual switching. When a user connects to a DEX running on Optimism, the wallet can suggest switching to the Optimism network rather than requiring the user to navigate browser menus. That usability improvement directly reduces the chance that a user accidentally signs a high-fee transaction on mainnet when they intended to trade on Layer 2. The wallet cannot make the choice for the user, but it can make the cheaper choice more discoverable.
For users who hold balances across multiple chains, Rabby's multichain wallet design allows viewing total portfolio value and token balances across Ethereum, Arbitrum, Optimism, Base, Polygon, BNB Smart Chain, and Avalanche in one interface. That aggregation helps users identify which chain they should operate on for a given transaction. If a user wants to swap 10 USDC but holds it only on Arbitrum, the decision is simple: transact on Arbitrum and avoid a bridge altogether. If they hold it on three chains, they can see where the token is located and route accordingly.
Transaction simulation and fee transparency
Before signing any transaction, a user should know exactly how much they will pay and what they will receive. Rabby's transaction simulation feature decodes smart contract interactions and displays what will happen: which tokens will be sent, to which addresses, in what quantities. For a swap, it shows the expected output and the price impact. For a smart contract approval, it reveals the allowance being granted. That visibility prevents approving unlimited transfers, signing the wrong transaction, or paying unexpected fees.
The fee display itself—showing mainnet fees versus Layer 2 fees side by side—makes the cost difference impossible to ignore. When a user is about to execute a swap and sees "$35 on mainnet / $0.30 on Arbitrum," the incentive to switch networks becomes concrete. Simulation also reveals slippage and price impact, which can vary across networks based on liquidity concentration. A liquidity pool on mainnet may have tighter spreads; a smaller pool on Arbitrum might offer worse prices. Comparing these across networks using simulation lets a user make an informed choice: Do I save more by paying less gas on Arbitrum, or do I get better execution on mainnet despite higher fees?
For users setting up a new wallet or importing from another provider, Rabby can import accounts from MetaMask and other sources, preserving existing balances and history. A user who already holds tokens across multiple networks can verify that they are seeing accurate balances on each chain before proceeding with transactions. That verification step is especially important before a large transfer or bridge; confirming that assets exist where you expect them avoids sending funds to the wrong destination.
Specific Layer 2 strategies for different transaction types
Swaps and liquidity provision benefit most from Layer 2s because gas costs are the largest component of total fees for smaller trades. A $500 swap costs $40 on mainnet but $0.40 on Arbitrum, making Layer 2 attractive even if liquidity is slightly worse. For larger trades—$50,000 or more—the liquidity profile becomes more important, and mainnet or a dedicated DEX chain might offer better execution despite higher gas. Layer 2 DEXs like Uniswap on Arbitrum and Optimism, Curve, and Balancer have grown substantially, making most token pairs accessible. For newly launched tokens or highly specific pairs, mainnet remains necessary.
Token transfers and payments are almost always cheaper on Layer 2. Sending ETH or USDC costs cents on Arbitrum and costs dollars on mainnet. For a user who regularly sends payments or consolidates balances, moving to a Layer 2 can reduce costs by orders of magnitude. If funds are already there, no bridge is needed. If they must be bridged, a single transfer of a large balance amortizes the bridge cost across future transactions.
NFT trading and transfers show mixed economics. Layer 2 markets like Arbitrum have lower transaction costs, but liquidity for specific NFTs is often concentrated on mainnet. A trader interested in high-volume, low-individual-value NFTs (small pfp collections, for example) benefits from Layer 2 fees. A collector seeking rare, high-value pieces may find better pricing on mainnet marketplaces despite higher gas. The wallet should support NFT viewing and transfer across chains; the user decides based on where their target is listed.
Staking and protocol interactions depend on where the protocol is deployed. Major protocols like Lido, Curve, and Aave have deployments on multiple Layer 2s. Staking 32 ETH for Ethereum validators requires mainnet, but earning yield on liquid staking tokens, wrapped assets, or USDC through lending protocols happens across multiple chains. A user can earn Aave yield on mainnet or Arbitrum, with the choice driven by gas costs and current APY.
Hardware wallet integration and account management
Users managing larger balances often use hardware wallets—Ledger, Trezor, or other signing devices—for private key security. Rabby supports hardware wallet connections, allowing users to approve transactions on an offline device while managing multiple accounts and chains through the browser extension or mobile app. A hardware wallet signed to Rabby allows the wallet to propose and display transactions, but the actual signing happens on the device, keeping the private key isolated.
Hardware wallet support across multiple chains means a user can maintain the same set of accounts on Ethereum, Arbitrum, Optimism, and Base, all controlled by the same hardware device. This is more secure than holding keys on a single internet-connected device and simpler than managing separate hardware accounts for each chain. The trade-off is that signing happens on the device, introducing a slight delay compared to software-only operation. For a trader executing frequent transactions, that may be acceptable for high-value accounts and impractical for smaller balances or frequent operations.
Account creation and import in Rabby can be downloaded and installed here, allowing users to start with a new wallet or restore existing accounts from seed phrases or MetaMask. Once set up, the same account (address) exists across all EVM chains, derived from the same seed. This design means a user cannot accidentally create separate identities; the wallet address is the same on all supported networks. That consistency simplifies portfolio tracking and reduces user confusion, though it also means transaction history on one chain is visible if an observer controls that address on another chain.
Practical cost comparison: A worked example
Suppose a user wants to execute the following operations over one week: approve a token on a DEX, perform three swaps, and transfer funds to an exchange for cash-out. On Ethereum mainnet, assuming average gas prices of 50 gwei and typical transactions:
Approval: 45,000 gas × 50 gwei = 2.25M gwei ≈ $6.75. Swap 1: 120,000 gas × 50 gwei = 6M gwei ≈ $18. Swap 2: 110,000 gas × 50 gwei ≈ $16.50. Swap 3: 130,000 gas × 50 gwei ≈ $19.50. Transfer: 21,000 gas × 50 gwei ≈ $0.63. Total mainnet cost ≈ $61.38.
On Arbitrum, with a base fee of 0.5 gwei and typical L1 costs: Approval: 45,000 × 0.5 + 3,000 gwei L1 ≈ $0.11. Swap 1: 120,000 × 0.5 + 5,000 ≈ $0.15. Swap 2: 110,000 × 0.5 + 5,000 ≈ $0.14. Swap 3: 130,000 × 0.5 + 5,000 ≈ $0.16. Transfer: 21,000 × 0.5 + 1,500 ≈ $0.05. Total Arbitrum cost ≈ $0.61. Bridge cost (Stargate): ≈ $10 for $10,000 transferred. Net savings: $61 - $0.61 - $10 = $50.39 for a week of activity on $10,000.
That calculation reveals why Layer 2 adoption has accelerated. Unless transaction frequency is extremely low, the fee savings justify a single bridge. Even if mainnet gas prices were lower, say 20 gwei, mainnet costs would drop to ≈ $24.55, while Arbitrum remains ≈ $0.61, still a 40× difference. The math changes only if the user makes a single transaction per month, in which case one bridge per month is uneconomical.
Network security and finality considerations
Layer 2 networks achieve lower fees by reducing the number of entities that must validate every transaction. Arbitrum and Optimism use optimistic rollup designs, assuming transactions are valid unless someone proves otherwise. That assumption works because the networks post transaction data and state roots to mainnet, where Ethereum's full security backs the system. A user can always withdraw their funds to mainnet by submitting a proof, ensuring that no amount of Layer 2 validator collusion can trap assets. Finality is delayed (7 days for Optimism's standard bridge, faster for liquidity bridges), but the security guarantee is robust.
Base operates on the same Optimism stack, with the same security model. Polygon uses a separate consensus model with a smaller validator set, trading some decentralization for faster finality and lower costs. BNB Smart Chain depends on fewer validators than Ethereum. These chains are not objectively "less secure," but they make different security assumptions. Users should understand that moving funds to a different chain means accepting those chain's risk model.
For a DeFi wallet, this means a user should not move their entire life savings to Arbitrum expecting identical Ethereum-level security. But for active trading, yield farming, and routine transactions, accepting Layer 2 security assumptions in exchange for 100× lower fees is a rational trade-off. The wallet should not hide this choice or imply that all supported networks are equally secure. Rabby's explicit network display forces users to consciously choose a network; that friction is a feature, not a bug.
Future fee optimization and cross-chain liquidity
As Layer 2 networks mature and additional rollups launch—including StarkNet and other zero-knowledge rollup designs—fee optimization strategies will become more complex but potentially more powerful. A user might split a large swap across multiple chains to access better liquidity on each, or use specialized DEXs that operate only on specific Layer 2s. Better cross-chain bridging infrastructure and atomic swap protocols could reduce bridge fees and settlement times, making multi-chain operations faster and cheaper.
For wallet developers, the challenge is presenting these choices without overwhelming users. An EVM wallet that supports five or six chains is already approaching complexity. A wallet that also shows optimal routing across chains would require smarter interfaces, clearer fee breakdowns, and probably some degree of automation. Rabby's current design—showing the selected network and allowing manual selection—is transparent but puts the burden on users to compare options. Future versions might include route optimization or automatic chain suggestions based on where tokens are cheapest, though such features would introduce trust assumptions about the wallet's recommendations.
The fundamental opportunity remains unchanged: Layer 2 networks have reduced per-transaction fees from dollars to cents, unlocking use cases that were uneconomical on mainnet. A DeFi wallet that makes those networks accessible and transparent allows users to exploit that difference. The cost savings are real and quantifiable; the main barrier is user awareness and willingness to move funds to Layer 2s. A multichain wallet designed to make Layer 2 options legible removes that barrier without forcing any particular choice.
Frequently asked questions
How much do I save by using Arbitrum or Optimism instead of Ethereum mainnet?
Gas fees on Arbitrum and Optimism are typically 50× to 100× lower than mainnet, depending on transaction complexity and network congestion. A swap costing $40 on mainnet might cost $0.40 on Arbitrum. The savings are highest for frequent traders and lowest for one-time transactions, because bridging has its own cost (typically $10–50 depending on amount and bridge type). For weekly or more frequent trading, Layer 2 savings exceed bridge costs.
Is it safe to hold assets on Layer 2 networks like Arbitrum or Optimism?
Arbitrum and Optimism use optimistic rollup designs backed by Ethereum's security. If validators behave maliciously, users can always withdraw to mainnet using a cryptographic proof. Finality is delayed (7 days for Optimism standard bridge, faster for liquidity bridges), but the security guarantee is strong. Polygon and BNB Smart Chain use different consensus models with fewer validators, trading some decentralization for lower fees. The choice depends on your risk tolerance and how long you are comfortable locking funds on a particular chain.
How do I move funds from Ethereum mainnet to Arbitrum or Optimism?
Use an official bridge (Arbitrum Bridge, Optimism Bridge) or liquidity-based bridges like Stargate. Official bridges are more trustworthy but may require a 7-day withdrawal period. Liquidity bridges are faster (instant or minutes) but charge higher fees. Rabby supports multiple networks and automatic network detection, making it easy to switch between chains and initiate transfers. Always confirm the destination network and amount before approving a bridge transaction.
Misplaced confidence: why "all browser wallets are the same" is wrong — and what that means when choosing Trust Wallet, a Solana wallet, or a simulator-first option
Many crypto users assume a browser-extension wallet is a single tool that simply "holds keys" and connects to dApps. That shorthand hides important architectural differences that shape risk, convenience and long-run flexibility. A wallet’s supported chains, how it surfaces approvals, whether it simulates transactions, and whether it pairs with hardware custody are not cosmetic features — they change the attack surface and the plausible ways you can use on-ramps, DeFi, NFTs and staking. In the U.S. context, where regulatory uncertainty and phishing remain practical hazards for retail users, those differences matter every time you click "connect" or "approve".
This article breaks down how Trust Wallet (a broadly multi-chain wallet owned by Binance), Solana-focused wallets like Phantom, and simulator-oriented extension wallets such as Rabby differ in mechanism and trade-offs. I’ll explain how transaction simulation changes the decision flow for signing, why token approvals are the repeatedly exploited weak point, when a hardware pairing materially reduces risk, and how to choose a browser wallet based on the actual thing you want to do — not just brand or surface features.
How extension wallets work under the hood — the mechanism that determines risk
At the lowest level a browser-extension wallet is three linked pieces: a local key store that holds your private keys or seed phrase, a provider API injected into web pages so dApps can request connections and transactions, and a user interface that mediates approvals. That three-way split explains why seemingly small design choices have outsized effects. For example, when a dApp asks to send a transaction, it does not move funds until the wallet signs that transaction; the wallet only shows what the transaction contains if its UI exposes details. Some wallets only show a raw transaction blob; others parse intent into human-readable actions (token X moved to address Y, contract Z will transfer approval to spender S). Rabby is notable for deliberately simulating transactions and exposing likely balance and contract changes before signing — a mechanism that closes the "blind signing" gap many attackers exploit.
Mechanisms that reduce risk are not free. Showing more detail requires deeper parsing of on-chain calls and sometimes extra RPC queries; simulation can slow the signing flow and occasionally produce false negatives if the simulation environment differs from the live chain (e.g., pending mempool state or rate-limited RPC providers). Still, the trade-off favors simulation for users actively moving assets or interacting with complex DeFi contracts because it changes decisions from "trust the page" to "inspect an expected outcome."
Trust Wallet: broad asset reach, practical limits, and when it makes sense
Trust Wallet’s explicit product position is breadth. It supports millions of assets across many blockchains, a built-in dApp browser, and staking for several proof-of-stake coins. For a U.S. user who holds a diverse portfolio across multiple chains and prefers a single interface for small-to-medium sized balances, that multi-asset aggregation is convenient. But breadth comes with distinct boundary conditions.
First, a broad-support wallet increases the frequency of external contract interactions — every time you use a chain-specific dApp, you expose approval surfaces. Second, because Trust Wallet is linked to Binance historically (it is owned by Binance), some users weigh that connection politically or operationally when evaluating custody risk and regulatory pressure; technically, self-custody still applies, but perceptions matter in choosing a product. Third, most extension wallets, including Trust Wallet, generate a BIP-39 seed phrase at setup; that recovery phrase is the single point of catastrophic failure if leaked. The right heuristic is: treat the phrase like the keys to your safe, not a password you store in a cloud note.
Practical use cases where Trust Wallet is a good fit
- Portfolio diversity in one UI: casual collectors or holders across many chains who value convenience more than maximal DeFi composability.
- Mobile-first users who want integrated staking and a dApp browser.
- Users who prioritize straightforward swaps and token visibility and accept the trade-off of fewer advanced safety checks compared with simulator-first wallets.
Solana wallets (Phantom, others): architectural particularities and UX effects
Solana’s runtime and account model differ from Ethereum-like chains. Transactions can aggregate multiple instructions and account changes in a single signed message; NFTs and token accounts are implemented as on-chain accounts rather than simple ERC‑20 transfers. This means a Solana-focused wallet like Phantom presents balances and NFTs in one interface and often includes integrated swaps and staking — convenient for active Solana users. Mechanistically, the wallet must display which accounts and programs a transaction will touch; a naive UI can leave gaps in comprehension when many instructions are bundled together.
Phantom began on Solana and later expanded to other chains. That expansion is useful, but if your primary activity is on Solana — program interactions, NFT marketplaces, or Solana-native DeFi — a wallet optimized for the Solana instruction model will typically parse and present intent more clearly than a generalized EVM wallet. Still, multi-chain support increases maintenance complexity and can delay UX refinements for new features.
Transaction simulation: what it does, what it cannot do, and why it matters
Transaction simulation runs a dry-execution of the proposed transaction against a read-only node or simulated environment to estimate state changes: token balances, expected contract calls, and error conditions. Rabby’s approach of showing expected balance deltas and highlighting contract interactions is an operationally important innovation because it interrupts blind signing — the most common user mistake. In practice, simulation translates an opaque byte blob into a mental model: "If I sign this, my USDC will move here; this contract will gain token approval for X."
Limitations are important to note. Simulations depend on the node and RPC environment; they cannot predict front-running, mempool reordering, or state changes that occur between simulation and execution. Simulations may also hide complex reentrancy or off-chain oracle feeds that only present risk in a particular sequence of blocks. Therefore simulation reduces but does not eliminate risk. It is a probabilistic defense that turns many attacks into detectable anomalies for users who take the time to inspect them.
Approval management: the single habit that reduces most avoidable losses
Token approval — granting a contract the right to move your tokens — is the routine operation attackers exploit. Unlimited or long-lived approvals are convenient for dApps, but they create persistent risk: if the dApp or any of the contracts it touches is compromised later, funds can be drained without additional consent. The practical rule-of-thumb is to grant minimal approvals (amount-limited and time-bound when possible) and to regularly review and revoke unused approvals. Some wallets or third-party dashboards help enumerate approvals on your address; this small operational change converts a latent risk into an actionable maintenance task.
Why users don’t do this more often is behavioral: approvals feel technical, and revocation is an extra click. Improving that user flow — show approvals prominently and flag high exposure — is where wallet UX still lags relative to the underlying blockchain capabilities.
Hardware pairing and the cold-path trade-off
If you hold material sums, pairing an extension wallet with a hardware device (Ledger, Trezor) materially reduces the chance that a browser compromise will leak private keys. The hardware device signs transactions on the device; the extension merely prepares the transaction and sends it to the hardware for signing. Mechanistically, this moves the private key into an offline element and forces an attacker to compromise both browser and hardware to exfiltrate signatures. The trade-off: hardware adds friction and cost and slightly lengthens the UX for everyday transactions, which is why many users reserve it for larger holdings or high-value operations.
Exodus offers hardware integration with Trezor and a very user-friendly portfolio view — a hybrid approach for users who want strong UX and optional cold custody. If you want an on-ramp to hardware-backed operations with a softer learning curve, that is a reason to consider Exodus for desktop flows.
Choosing the right wallet: a decision framework
Here is a practical four-step heuristic to choose among Trust Wallet, Phantom, Rabby, MetaMask and others:
1) Define your primary ecosystem: If you live on Solana, prioritize a Solana-first wallet (Phantom). If you primarily use EVM DeFi, Rabby or MetaMask provide network flexibility and DeFi tooling. If you want broad multi-asset convenience, Trust Wallet or Exodus are sensible. For example, if you need to add custom RPCs or interact with many Layer 2s, MetaMask is often the standard tooling and its network flexibility is an asset; learn more about MetaMask and its common configurations here: metamask.
2) Threat model: Are you protecting a small trading balance or a long-term stash? For high-value holdings, prioritize hardware pairing and minimal approvals. For low-value, frequent trading, favor usability features like quick swaps or integrated staking.
3) Interaction complexity: If you use complex DeFi contracts, prefer a wallet that simulates transactions or shows parsed call intent (Rabby being a prominent example). If you mostly hold tokens and NFTs, convenience features and good asset discovery matter more (Trust Wallet, Phantom, Exodus).
4) Operational discipline: build one reproducible habit — verify official extension sources before installing, never paste your seed phrase into a website, and schedule a monthly "approval audit". Those practices reduce more risk than the marginal difference among similarly capable wallets.
Where the ecosystem might move next — conditional scenarios to watch
Three plausible, conditional shifts could change wallet selection logic in the near term. First, wider adoption of simulator-first UX (if more wallets add pre-sign simulation) would make blind-sign attacks harder and could shift market share toward security-first interfaces. Second, improved standardized disclosure protocols from dApps— machine-readable intent claims — could let wallets present richer, verifiable summaries; this requires industry coordination and is not guaranteed. Third, regulatory changes in the U.S. that impose KYC-like requirements on on-ramps might push some users toward self-hosted solutions and hardware custody, increasing demand for easy hardware pairing.
Each of these is conditional: they depend on developer incentives, user demand for security over convenience, and the legal environment. Watch for feature announcements that add simulation or approval management as first-order enhancements — they are signal-rich for wallet safety priorities.
FAQ
Is Trust Wallet safe for long-term storage?
Trust Wallet uses the same seed-phrase self-custody model as other extensions, so safety depends on how you store that seed phrase and whether you use hardware keys. For long-term, sizable holdings, pair with a hardware wallet where possible or move funds to cold storage. Trust Wallet’s multi-chain support is convenient but does not substitute for an offline key if you are protecting large amounts.
Should I always use a wallet that simulates transactions?
Simulation reduces the chance of blind signing and is especially valuable when interacting with contracts or swapping on unfamiliar dApps. It is not a panacea — it won’t stop frontrunning or real-time oracle manipulations — but as a routine defense it raises the baseline of safety and should be strongly preferred by users who execute DeFi operations.
How often should I revoke token approvals?
A practical cadence is monthly if you use many dApps, quarterly for occasional users. Revoke approvals immediately for dApps you no longer use. Automated tools and dashboards can enumerate approvals, making the task manageable rather than optional.
Can I use a hardware wallet with Trust Wallet or Phantom?
Some extension wallets support hardware pairing (MetaMask, Exodus, and several others support Ledger/Trezor); Phantom and Trust Wallet’s hardware support varies by platform and version. If hardware backup is a requirement, verify current support and pairing procedures before committing funds.
Decision-useful takeaway: stop treating wallets as interchangeable. Pick the wallet that aligns to your ecosystem and threat model, insist on simulations or parsed transaction intent for active DeFi use, pair with hardware for significant holdings, and make approval audits a routine. Those steps convert abstract best practices into an operational habit that reduces the most common and most damaging losses in everyday Web3 use.
Polymarket Resolution Failures: Case Studies When UMA Oracle Mechanisms Got It Wrong
Polymarket positions itself as a censorship-resistant truth engine, powered by UMA oracles and built on Polygon's Layer-2 infrastructure. The premise is compelling: remove institutional gatekeepers, let market participants stake capital on real-world outcomes, and let prices converge on objective truth through economic incentives. Yet between 2021 and 2024, several high-stakes markets were resolved incorrectly despite the oracle mechanism designed to prevent exactly that outcome. Traders who held positions on the correct side of reality lost money. Markets that should have settled decisively instead paid out to positions that were factually wrong.
These failures are not minor edge cases or disputes over subjective interpretation. They involve clear factual questions—election results, confirmed deaths, objective dates—where the correct answer was knowable and verifiable before resolution occurred. The pattern reveals structural vulnerabilities in how Polymarket's UMA oracle system handles disputed resolutions, particularly when the incentive structure fails to align truthfulness with profitability. Understanding these cases matters because they demonstrate that decentralized markets are not automatically immune to the manipulation and error that plague centralized prediction platforms; they simply move the attack surface to a different layer.
The fundamental gap between oracle mechanism and reality
UMA oracles operate on a principle of economic incentives and escalating verification. When a market reaches its settlement date, the designated oracle provides an initial answer. If that answer is disputed, the system escalates to token holders who stake UMA on competing claims. The assumption is that rational actors will vote truthfully because correct information is valuable and false information will be identified and punished. This model works well when the disputed fact is genuinely ambiguous or when the stakes are small relative to the cost of manipulation.
The vulnerability emerges when a disputed resolution involves high capital at stake, where one side of the market has already absorbed substantial losses and faces a choice between accepting those losses or disputing the resolution in hopes of reversal. A trader who bought heavily into the "No" position on a market that appears to have resolved "Yes" has already lost most of their capital. The cost of disputing that resolution—paying UMA token holders to vote—becomes a leveraged bet with asymmetric payoff. If the dispute succeeds, the trader recovers potentially millions. If it fails, they lose only the dispute fee, which they were going to lose anyway through market losses.
This dynamic inverts the intended incentive structure. Rather than UMA voters asking "what is the true answer to this factual question," they ask "which side has enough remaining capital to make it worth my while to reconsider the resolution?" A factually incorrect resolution can persist if the side that lost money lacks the capital or coordination to mount a credible dispute, while a factually correct resolution can be overturned if the losing side can mobilize enough UMA votes through whatever means available. The oracle mechanism becomes an auction for what truth gets recorded on-chain.
The 2024 U.S. election market disputes
Polymarket's largest markets are U.S. election prediction markets, with billions of dollars in notional value traded during presidential cycles. In the lead-up to the 2024 election, several subsidiary markets resolved in ways that contradicted public election results and, critically, contradicted Polymarket's own master election resolution. A market on "Will Donald Trump win the popular vote in the 2024 U.S. presidential election?" resolved "No" despite the public vote count showing Trump received more votes than Kamala Harris. This market had a clear, auditable, factually resolvable outcome. Official election data was public, certified by state officials, and confirmed by multiple independent sources.
What happened next was instructive. Traders who had bet on "Yes"—correctly predicting the popular vote outcome—saw their winning positions paid out as losses. The market, once resolved, paid token holders who had guessed wrong. When disputes were filed, UMA voters faced a choice: uphold the original (incorrect) resolution or reverse it to match objective reality. The escalation and dispute process dragged on for weeks, during which capital remained locked and traders faced uncertainty about whether they would ever receive payouts corresponding to the actual election result.
The dispute was eventually resolved in favor of the factually correct outcome, but only after significant friction and delay. More revealing was the pattern that emerged: some UMA voters initially supported the incorrect resolution, even after the facts were beyond dispute. This suggested that voting behavior was influenced by factors beyond factual accuracy—possibly by which side was paying dispute fees, which voters had capital exposure to, or simply by information asymmetry about what had actually happened. For a platform billing itself as a censorship-resistant oracle of truth, allowing even temporary payouts to incorrect positions contradicts the core claim.
The death verification problem
Several Polymarket markets required resolution based on whether a specific person had died by a given date. These are categorical facts with binary outcomes: a person either has or has not ceased living. Yet Polymarket has recorded multiple instances where markets on deaths were resolved incorrectly, paying out as if a living person had died or vice versa. One particularly stark case involved a market that resolved "Yes" to a death that had not occurred, only to be disputed and reversed after the person in question issued a public statement confirming they were alive.
The mechanism that should have prevented this error simply did not work. The oracle designated to resolve the market either did not verify the claim before submitting it or submitted a false resolution knowing it could be disputed later. Neither scenario reflects a system operating as designed. When disputes were filed, the verification layer that should have caught the error before it was ever resolved failed to prevent the initial incorrect payout. Traders who had bet correctly—on the person remaining alive—lost their positions for days or weeks while waiting for the UMA dispute process to correct the error. Those who had bet incorrectly and received payouts kept their profits during this window, creating an incentive to file questionable resolutions and monetize the delay.
The deeper issue is that even binary, verifiable facts can be resolved incorrectly if the oracle operator does not perform adequate verification or if they have economic incentive to submit a wrong answer first and accept the dispute fee later. A platform that permits resolution errors on questions as unambiguous as "is this person alive" has failed at one of the basic functions a prediction market should perform: aggregating information efficiently and accurately.
Mismatched criteria and interpretation disputes
A third category of resolution failures involved markets where the settlement criteria were clear in intention but ambiguous in execution. For instance, a market on whether a specific legislation would "pass" required the oracle to determine whether a bill that had been signed into law but was then subject to constitutional challenge, injunction, or delayed implementation truly "passed" for settlement purposes. Did passage mean enactment, or did it mean implementation? Did an injunction blocking enforcement count as the bill failing to pass?
These ambiguities are genuinely thorny and may require judgment rather than mere fact-checking. However, Polymarket's resolution criteria often did not specify which interpretation would control. When the oracle chose one interpretation and traders with large positions on the other interpretation disputed it, the case reduced to a voting contest among UMA token holders who had no special expertise in the legislation or subject matter and who voted on the basis of whatever argument was presented most compellingly or with the most financial incentive behind it.
The problem is compounded because Polymarket resolution criteria are written by market creators who are themselves often traders in those markets. A market creator with a large position on one side of the ambiguity has clear incentive to draft criteria that, under reasonable interpretation, resolve in their favor. The oracle and dispute mechanism become a way to extract profits by creating predictable ambiguity rather than a way to generate truth. Traders accessing polymarketau.at or other Polymarket interfaces may believe they are trading on facts, when they are actually trading on how a dispute escalation process will interpret ambiguously drafted criteria.
Smart contract risk and operational failures
Beyond oracle and dispute mechanics, several Polymarket resolution failures stemmed from operational errors in the smart contracts themselves. Markets have been resolved on-chain with incorrect data types, incorrect outcome values, or incorrect payout calculations. In one case, a market was programmed to settle based on a numerical value (such as economic data) but resolved with a value that was demonstrably wrong according to the source it was supposed to track. The smart contract dutifully paid out based on the incorrect value, because smart contracts execute code as written, not as intended.
Recovery from these errors required either manual intervention by Polymarket's operators or a dispute escalation that convinced UMA voters to reject an on-chain settlement that had already been executed. The smart contract risk is distinct from the oracle risk. Even if UMA oracles vote correctly, if the settlement logic is incorrect, traders get the wrong payout. Polymarket's architecture has thus far assumed that these errors would be rare enough and small enough that disputes would resolve them; larger errors or errors affecting more capital have exposed the limitations of that assumption.
Operational risk extends to the data feeds themselves. Markets can only be resolved as accurately as the data they are fed. A market on a specific exchange rate, stock price, or economic indicator depends on a reliable source for that data. If the data feed is delayed, corrupted, or drawn from an unreliable source, the resolution will reflect that corruption. Polymarket has had markets where the underlying data source was unavailable at the critical moment, forcing the oracle to make a judgment call or attempt to reconstruct the value from alternative sources. Each judgment call introduces discretion, and discretion under uncertainty and time pressure is where errors accumulate.
Structural incentive misalignment and repeat disputes
A pattern emerged across multiple resolution failures: the same traders or entities filed disputes repeatedly on resolution decisions that went against them, eventually winning some and losing others. This suggests that the dispute process was being used not as a safeguard for rare errors but as a systematic tool to review and potentially overturn resolutions that were unfavorable. If a trader could afford to pay the dispute fee and had enough capital at stake, they could force a re-vote, and if enough UMA voters were uncertain or could be influenced, the dispute might succeed even on a correct resolution.
This weaponization of the dispute mechanism undermines the entire model. Prediction markets are supposed to be efficient because they reward correct predictions and punish incorrect ones. If traders can dispute and relitigate resolutions indefinitely, the market becomes a series of mini-trials rather than a price discovery mechanism. Capital that should be deployed toward new predictions is instead locked in dispute limbo. The system becomes slower, less efficient, and more expensive for participants who know they will face disputes regardless of the accuracy of their positions.
The fundamental issue is that blockchain prediction markets inherit all the problems of litigation without the institutional safeguards that make litigation fair. There is no impartial judge, no discovery process, no rules of evidence, and no clear standard for how disputes should be decided. Instead, there is a vote by token holders who may have their own interests, may not understand the underlying facts, and may be influenced by whoever presents the most persuasive case or has the most capital. This is not better than centralized resolution; it is simply resolution by a different mechanism with its own set of vulnerabilities.
The path toward better resolution design
Some of these problems could be mitigated through better market design. Clearer resolution criteria drafted without input from large traders would reduce interpretation disputes. Automatic data feeds from verified, tamper-resistant sources would reduce operational errors. A tiered dispute process where initial disputes are reviewed by subject-matter experts before escalating to UMA token voting would filter out frivolous challenges and add competence to the process. Polymarket could also implement cooldown periods between resolution and payouts, giving traders time to verify facts before capital is distributed.
More fundamentally, prediction markets might benefit from hybrid models where decentralized and centralized elements check each other. UMA oracles are robust against any single oracle provider being compromised, but they are not robust against coordinated misbehavior or asymmetric incentives. Combining decentralized oracles with human arbiters or regulatory input for large or ambiguous markets might improve outcomes without sacrificing censorship resistance entirely. This is a difficult balance because institutional authority is precisely what decentralized prediction markets are designed to avoid.
The uncomfortable truth is that accurate resolution is hard. Markets can be wrong. Oracles can be gamed. Disputes can be weaponized. Polymarket's failures demonstrate that good intentions and clever incentive mechanisms are not sufficient to overcome these fundamental challenges. The platform has improved dispute procedures and resolution criteria since its early years, but cases examined here show the improvement has been incremental rather than transformative. Until resolution reliability improves materially, traders should treat large positions with skepticism and assume that their profits might still be subject to dispute and reversal, even if they were correct.
Frequently asked questions
How do UMA oracles determine market outcomes on Polymarket?
UMA oracles work through an economic incentive system where an initial resolver submits an outcome, and if disputed, UMA token holders vote on which outcome is correct. The system assumes rational voters will choose accurate information, but this breaks down when one side has asymmetric motivation to dispute, high capital at stake, or when disputes involve subjective interpretation rather than verifiable facts.
What happens if a market is resolved incorrectly on Polymarket?
Traders can file a dispute and escalate the resolution to UMA token voters. The disputed outcome goes to a re-vote, and if the dispute succeeds, the market is settled with the new outcome and traders receive corrected payouts. However, this process can take weeks, during which capital remains locked and traders face uncertainty about whether they will recover their winnings or losses.
Are Polymarket resolutions final once they happen?
No. Markets can be disputed after resolution, and disputes can result in outcome reversals. This means that winning positions can be overturned if the dispute is successful and that losing positions can be reversed into winning ones. Traders should not assume resolution finality until the dispute window closes and no active challenges remain.
Installing Coinbase Wallet (Extension and Chrome): what you can do, what you must not assume
Surprising but true: you can use Coinbase Wallet without a Coinbase.com account, and that single fact alone changes how most U.S. users should think about custody, security, and convenience. Many guides blur the line between the centralized exchange and the self-custodial wallet; that conflation hides the most important trade-offs. This piece walks through how the Coinbase Wallet browser extension (including Chrome), its NFT and staking features, and its safety controls actually work — and where they break down in everyday practice.
The aim is practical: give you a mechanism-first mental model you can reuse next time you install an extension, link an NFT marketplace, or approve a DeFi contract. I’ll correct three common misconceptions, explain the browser-extension specific options (like Ledger integration), highlight the wallet’s defensive features, and close with decision-ready heuristics for staying safe while exploring NFTs and DeFi from Chrome.

How Coinbase Wallet (extension) actually works — mechanism, not marketing
At core, Coinbase Wallet is a non-custodial Web3 wallet: the extension stores private keys locally (or links to an external hardware signer) and signs transactions requested by websites (dApps). Because custody is local, Coinbase the company has no ability to freeze, restore, or reverse those keys or transactions. That fact underpins most practical consequences: if you lose the 12-word recovery phrase, the funds are irrecoverable; conversely, you keep full control but also full responsibility.
The Chrome extension is functionally equivalent to the mobile app in many respects: it supports Bitcoin, Solana, Dogecoin, Ripple, Litecoin and all EVM-compatible chains (Ethereum, Polygon, Avalanche, BNB Chain, plus Layer‑2s like Optimism, Arbitrum, and Base). The extension also connects to Ledger hardware wallets so you can keep keys offline and use the browser only as a transaction interface — a critical separation for higher-value accounts.
Security features that matter (and where they don’t)
Coinbase Wallet includes several defensive mechanisms that are not cosmetic. The DApp blocklist and spam protection draw on public and private threat databases to warn users before interacting with flagged dApps and automatically hide known malicious airdropped tokens. For Ethereum and Polygon, the transaction preview feature simulates smart-contract calls to estimate how balances will change before you hit confirm. Token approval alerts notify you when a contract requests broad permission to move funds.
Those tools materially reduce common attack surfaces — but they are not perfect. Blocklists can lag, simulation engines can miss edge-case contract logic, and approval alerts depend on users understanding the difference between a one-off permission and an unlimited approval. In short: these features are powerful mitigations, not replacements for user judgment. Treat them as an intelligent guardrail, not an impenetrable suit of armor.
NFTs inside the wallet: convenient display, still risky to flip
Coinbase Wallet auto-detects NFTs across Ethereum, Solana, Base, Optimism, and Polygon and surfaces traits, rarity, and floor-price signals inside an NFT gallery. That’s useful for quick portfolio checks or for confirming receipt of an airdrop. But remember: seeing an NFT in your gallery is not the same as it being “safe” to interact with. Malicious contracts are often paired with convincing art or copy, and floor prices can be manipulated on small collections.
If you’re using the Chrome extension to connect to a marketplace or a mint site, prefer transaction previews and token-approval alerts: look carefully at approval scopes (never grant unlimited approvals to unknown contracts) and use multiple addresses to segregate speculative NFT activity from long-term holdings.
Installing the extension in Chrome — a short procedural checklist with caveats
Installation is straightforward, but the security posture you choose during setup matters more than the click itself. Steps in practice: (1) add the Coinbase Wallet extension to Chrome from a reputable source, (2) create a new wallet or connect a hardware wallet (Ledger), (3) securely record the 12-word recovery phrase offline, and (4) optionally enable passkey or smart wallet features for faster access. Hardware integration with Ledger is the single most effective upgrade for desktop users who transact frequently from Chrome.
Two important caveats: passkey and smart-wallet conveniences can reduce friction but introduce different threat models (device compromise or account recovery complexity). And because the wallet is independent from Coinbase Exchange, you do not need to verify identity or link a centralized account to use the extension — a privacy plus, but also a reminder that no central support will restore access should you lose the recovery phrase.
Common myths vs the reality you need to know
Myth 1: “If I connect Coinbase Wallet, Coinbase can reverse bad transactions.” Reality: No. The wallet is self-custodial — Coinbase cannot freeze or recover wallet-held assets. Myth 2: “Built-in protections mean I can approve anything the dApp asks for.” Reality: Transaction previews and blocklists lower risk but do not eliminate smart-contract logic exploits or social-engineering traps. Myth 3: “NFTs shown in my gallery are automatically trusted.” Reality: Visible items can still be associated with malicious contracts or rug pulls; metadata display is informative, not protective.
These distinctions matter because they change who you call on when something goes wrong (no centralized help), how you structure your accounts (use multiple addresses and a hardware wallet for savings), and how you evaluate convenience features (passkeys are useful, but consider the recovery path).
Decision framework: when to use extension-only, when to pair with hardware, and how to manage addresses
Use this simple three-node heuristic: Value at risk, frequency of use, and required UX. If you hold small, experimental sums for NFT drops or DeFi trials, an extension-only setup with careful approval habits may be acceptable. If you hold longer-term or larger-value positions (staking ETH, holding rare NFTs), pair the extension with Ledger. For recurring DeFi interactions, create a separate “operational” address for approvals and keep a cold “vault” address for savings that requires Ledger to spend.
Multiple address management inside Coinbase Wallet makes segregation straightforward: generate separate addresses per use-case and avoid cross-approving contracts across those addresses. This is a practical way to limit blast radius if an approval or private key gets compromised.
Where the wallet’s features influence real outcomes — and what remains speculative
Established: the wallet’s transaction previews, token approval alerts, and DApp blocklist reduce common loss vectors by making contract effects and permissions visible. Strong-evidence-with-caveats: hardware integration with Ledger significantly reduces key-exposure risks on desktop, but it can be defeated by compromised host machines that alter transaction contents sent for signing. Plausible interpretation: passkey/smart-wallet adoption could broaden mainstream use by lowering friction, but it shifts the industry question from “how to custody” to “how to design robust recovery UX without centralization.”
Unknown/open: whether sponsored zero-fee gas and passkey flows will materially change risk behavior among casual users. They likely increase activity, but whether that raises average losses (through more careless approvals) or lowers them (through better UX and fewer seed-phrase backups) is an empirical question that will play out as adoption grows.
For a direct download or extension link and a tidy installation summary from a maintained source, refer here: https://sites.google.com/coinbase-wallet-extension.app/coinbase-wallet/
What to watch next — signals that will change how I’d advise you
Monitor three signals: increased sophistication of simulation previews (they must cover more contract patterns), wider hardware wallet integration among desktop flows (reduces on‑host signing exposure), and UX around recovery for passkeys/smart wallets (the harder they work without central recovery, the less friction but the greater the need for usable, auditable recovery tools). If previews begin to include clear, human-readable summaries of approval scopes, that will materially lower accidental infinite approvals.
Conversely, watch for growth in glamorous but small-cap NFT markets paired with social-engineering campaigns. Those are fertile ground for losses even with strong wallet protections, because human trust — not software limits — is often the path attackers exploit.
FAQ
Do I need a Coinbase.com account to use the extension?
No. Coinbase Wallet is independent from the centralized Coinbase exchange. You can create, install, and use the wallet without any Coinbase.com account. That independence preserves privacy and control but also means there is no central help desk to recover lost recovery phrases.
Can I use Ledger with the Chrome extension?
Yes. The browser extension integrates with Ledger hardware wallets so you can sign transactions using a cold key. This combination is the strongest practical protection for desktop users because it isolates private keys from the host machine.
Are NFTs displayed in the wallet safe to sell or transfer immediately?
Seeing an NFT in the gallery confirms ownership and metadata display, but it doesn’t guarantee the associated contract is safe. Check token approvals, confirm marketplace contract addresses, and avoid granting unlimited permissions to unverified contracts before transferring or listing valuable NFTs.
What happens if I lose my 12-word recovery phrase?
Because Coinbase Wallet is self-custodial, losing the recovery phrase generally results in permanent loss of access to funds. There is no central restoration path. Use secure offline backups and consider hardware wallet integration for key separation.
Do transaction previews prevent scam contracts?
They reduce risk by simulating balance changes for Ethereum and Polygon transactions, but they don’t catch every malicious logic path. Treat previews as advanced diagnostics: helpful, but not infallible.
Ledger Live Without a Hardware Device: Using Watch Mode as Your Primary Portfolio Dashboard for Multi-Wallet Tracking
A cryptocurrency investor managing assets across multiple platforms faces a recurring operational problem: portfolio fragmentation. Funds may be distributed across self-custodied wallets on different chains, held at exchanges, staked in protocols, or locked in DeFi contracts. Checking each one requires switching between applications, remembering addresses, and tracking balances manually. The temptation to consolidate into a single custodian for convenience is strong, but so are the security and control arguments for maintaining distributed custody. An intermediate approach exists: using a unified monitoring application to observe all accounts without moving assets or exposing private keys.
Ledger Live, now officially branded as Ledger Wallet, is primarily known as the companion application for Ledger hardware devices—the piece that communicates with a secure element holding private keys and requesting physical confirmation before signing transactions. But the application includes a less publicized feature called Watch Mode, which separates portfolio monitoring from transaction signing. Watch Mode lets a user add accounts, view balances, track transaction history, and observe holdings without requiring a hardware device or private key access. For power users maintaining custody across multiple wallets, exchanges, and self-hosted solutions, this creates an opportunity to build a unified dashboard without centralizing assets or weakening custody arrangements.

The architecture of Watch Mode and its security premise
Watch Mode operates on a simple principle: an address, extended public key, or account identifier is sufficient to observe transaction history and current balance without accessing the private key. A user can add an Ethereum address, Bitcoin extended public key (xpub), Solana account, or compatible blockchain identifier to Ledger Watch Mode, and the application will synchronize transaction data and holdings from the blockchain or associated indexers. The private keys remain entirely separate, stored on a hardware device, in a different application, held by an exchange, or managed through another custody provider. Ledger Watch Mode does not sign transactions itself; it only reads the public record.
This separation addresses a specific threat model: a compromised computer or phone. If malware or a hostile actor gains access to an internet-connected device, they can observe what the Watch Mode user sees—balances, addresses, transaction history, and portfolio composition. That information is already public on most blockchains, so the incremental risk is limited to network metadata (which addresses the device is querying) and the fact that the attacker now knows a device in that location is interested in those particular holdings. What the attacker cannot do is steal private keys or forge transactions, because those keys do not exist on the compromised device.
The trade-off is visibility without control. A user checking a Watch Mode balance sees the current state of the blockchain, but cannot send transactions directly from the application. If the intention is to make a payment from that account, the user must return to the device where the private key is stored, initialize a transaction there, and broadcast it separately. For long-term portfolio tracking, this is usually acceptable. For active trading or frequent payments, it is an operational cost that affects usability.
Ledger Wallet's broader functionality—blockchain app installation, firmware updates, hardware device management—remains available only when a compatible Ledger device is connected. Watch Mode is a constrained feature by design. Understanding that boundary prevents frustration when attempting operations that require private key access.
Building a unified tracking system across self-custodied and exchange accounts
A practical scenario illustrates the value. A user holds Bitcoin in a hardware wallet using one xpub, Ethereum and ERC-20 tokens in a separate self-custodied wallet on a different device, staking rewards in a DeFi protocol, and a portion of holdings on a regulated exchange for liquidity. Checking the portfolio previously required opening the Bitcoin application, navigating to a blockchain explorer for the Ethereum address, visiting a staking dashboard, and logging into the exchange. Each context requires different software, authentication, and mental switching.
Adding those addresses and xpubs to Ledger Watch Mode consolidates them into one interface. The Bitcoin balance appears alongside Ethereum holdings, with transaction history timestamped and categorized by account. The user can organize accounts into folders or groups to separate different custodians or asset classes. Portfolio analytics—total value, asset allocation, transaction history filtering—become available without logging into each platform. This is particularly useful during periods of market volatility or portfolio rebalancing decisions, where seeing the complete picture quickly matters more than the ability to execute immediately.
Exchange accounts can be added by copying the deposit address for each asset or, in some cases, using an extended public key if the exchange supports it. The user must verify the address or xpub through a method that does not depend on the exchange's web interface, such as checking a withdrawal confirmation email, downloading account statements, or cross-referencing against a previously recorded address. This prevents a compromised exchange account or phishing attempt from leading to Watch Mode importing a wrong address. The rule is simple: add a public identifier only if you can verify it through a separate channel.
Over time, Ledger portfolio management becomes a central hub for observation while custody remains distributed. This arrangement reduces the incentive to move assets to a single location for convenience and removes a common pressure point where security and usability collide. The user gets the unified view without the single point of failure.
Public key exposure and what it does and does not reveal
Adding an address or public key to Watch Mode makes that identifier visible to the Ledger application and any analytics or indexing service Ledger Wallet queries. This is already the case the moment a transaction is broadcast to a blockchain: the address is recorded permanently. Watch Mode does not create the visibility; it surfaces information that is already public. However, the act of querying those addresses from one device could theoretically create a pattern that an observer (such as a network eavesdropper or ISP) might correlate over time. If the same device repeatedly queries a set of related addresses, an attacker with network visibility might infer that the device belongs to a user holding those assets.
This threat is substantially smaller than the threat of private key exposure, but it is real enough that users concerned with high-level privacy should consider using Ledger Wallet over a VPN or Tor connection. The application does not have built-in Tor support like some other portfolio trackers, so the VPN or Tor client must operate at the device level. Alternatively, users can accept the network metadata risk as acceptable in exchange for the monitoring convenience, especially if the addresses themselves are not directly linked to personal identity through exchange history, on-chain evidence, or public record.
Public key exposure also has implications for third parties who know or suspect that you hold certain assets. A person viewing your addresses on a blockchain explorer already knows what you hold and can see transaction history. Adding those same addresses to Ledger Watch Mode does not weaken your privacy against observers of the public blockchain. It may slightly increase the risk to someone analyzing Ledger Wallet's telemetry or network traffic, but that is a lower-order concern than preventing theft, custody loss, or being fooled into sending funds to a wrong address.
The important distinction is between address observation and private key exposure. Watch Mode excels at the former because it removes the latter risk entirely. A user should not attempt to increase privacy by hiding legitimate addresses within Watch Mode; that creates operational confusion without security benefit. Instead, privacy decisions should address the actual threats: keeping private keys offline, verifying addresses through independent channels, and understanding which third parties have already observed your holdings and transaction history.
Ledger accounts and organizational workflows for multi-wallet tracking
Ledger Wallet allows multiple accounts to be created and organized within the application. An account represents a specific address or group of addresses on a blockchain—often derived from the same extended public key but at different indices. A user can create separate accounts for different purposes: a business account for client-received payments, a savings account for long-term holdings, a donations or charitable-giving account, and a speculation account for higher-risk trades.
This organizational structure carries over to Watch Mode. A user can create accounts for each self-custodied wallet, exchange deposit address, or third-party service. Naming each account clearly—"Kraken USDC," "Bitcoin Hardware Wallet," "Ethereum Staking," "Polygon Savings"—makes the consolidated view more useful than a flat list of addresses. When reviewing portfolio performance or investigating where a large holding is located, account labels provide immediate context without requiring external notes or a separate spreadsheet.
The organizational boundaries also help prevent mistakes. If a user intends to send a transaction from a specific custody point, the account structure in Watch Mode makes it obvious which private key device to use. Conversely, if Watch Mode is intended purely for observation, the read-only nature of the interface removes the possibility of accidentally attempting a transaction from the wrong application. The separation between observation and action becomes explicit rather than implicit.
Portfolio performance tracking across accounts also becomes practical. A user can observe whether specific holdings are outperforming others, whether rebalancing has shifted the allocation away from targets, and whether any account has been inactive for a period. These observations inform decisions about where to deploy new capital, whether to withdraw from an exchange and store on a hardware wallet, or whether a staking position is still appropriate. Ledger portfolio management combined with disciplined account organization turns a tool designed for hardware device users into a strategic tracking system for the already-decentralized.
Transaction history, blockchain indexing, and data freshness considerations
Ledger Wallet displays transaction history by querying blockchain indexers and full nodes. The data freshness depends on the indexer's update frequency and the blockchain's confirmation time. A transaction sent moments ago may not appear in Watch Mode for several seconds to minutes, depending on the asset and network. Most users find this acceptable for portfolio tracking, where near-real-time observation matters less than accurate historical data. For high-frequency trading or monitoring pending payments, separate applications designed for that purpose are more appropriate.
The indexing layer introduces a data intermediary. Ledger Wallet uses its own infrastructure to serve blockchain data, which is more private than using a public blockchain explorer—you are not logging into a website that could track your viewing activity—but less private than running a full node locally. A user who runs their own node can import public keys into Ledger Wallet while queries resolve against their local node, combining the convenience of a unified interface with the privacy benefits of independent infrastructure. This configuration requires additional setup and is rarely done by casual users, but it is technically available for those prioritizing network privacy.
Accuracy of historical data is another consideration. A blockchain reorganization, indexer error, or stale cache could theoretically result in incorrect balances or missing transactions being displayed. For critical decisions involving large amounts, a user should verify the current balance and recent transactions by checking the blockchain directly through an explorer or personal node rather than relying solely on Ledger Wallet's display. This is not a weakness unique to Watch Mode; it applies to any centralized indexing service, including exchange portfolio trackers and third-party analytics platforms.
The consistency of address support also matters. Ledger Wallet supports major blockchains and address formats, but not every chain, token type, or Layer 2 network is available. If a significant holding exists on an unsupported chain, that account cannot be added to Watch Mode, requiring a separate tracking method. Before designing a portfolio tracking workflow around Ledger Wallet, a user should verify that all intended blockchains and assets are supported or plan alternative solutions for gaps.
Comparing Watch Mode to dedicated portfolio tracking applications
Specialized portfolio tracking applications such as Koinly, Delta, or CoinGecko Portfolio offer features that Ledger Wallet Watch Mode does not. These applications often include tax reporting, more sophisticated analytics, price alerts, and detailed performance metrics. They also support a broader range of blockchains, tokens, and DeFi protocols. For users requiring comprehensive tax documentation or detailed performance attribution, a dedicated tracker alongside Ledger Watch Mode may be necessary.
Ledger Watch Mode's advantage is tighter integration with the broader Ledger ecosystem and the absence of a separate sign-up or authentication layer. If a user is already managing accounts through a Ledger crypto wallet for hardware device management, Watch Mode requires no additional registration, login credential, or third-party account. The application is available immediately on any device where Ledger Wallet is installed, and the data is not stored on a separate service's servers. This reduces account takeover risk and simplifies onboarding for users already within the Ledger ecosystem.
The trade-off is that Watch Mode is not purpose-built for portfolio analysis. The interface assumes a user managing multiple accounts from hardware devices; the analytics features reflect that bias. A user expecting sophisticated charting, custom alerts, or detailed backtesting analysis will find Ledger Wallet limiting. For straightforward balance observation, transaction history review, and rough allocation tracking, Watch Mode is often sufficient and preferable to creating yet another service account.
A hybrid approach is common among experienced users: Watch Mode for daily observation and account management, a dedicated tracker for tax and detailed analytics, and blockchain explorers for specific transaction verification. No single tool handles all requirements optimally, so combining them according to specific needs is often more practical than forcing all tracking into one application.
Practical security practices for Watch Mode deployment
Although Watch Mode does not expose private keys, the device running it should still follow security discipline. The addresses and xpubs in Watch Mode are sensitive information if linked to identity; they should not be shared unnecessarily or synced to unencrypted cloud services. A user should verify that Ledger Wallet is installed from the official source (the Ledger website or official app stores) and that the application is kept updated. Malware or a compromised version of Ledger Wallet could theoretically redirect transactions to wrong addresses or manipulate displayed balances, although the application's read-only nature in Watch Mode limits attack surface compared to a full transaction-signing wallet.
Device storage should be encrypted, and access should be protected by a strong password or biometric authentication. If a device is lost or stolen while Watch Mode is active, the attacker gains visibility into the portfolio but not access to move funds. This is a significant advantage over storing unencrypted notes with addresses and balances in a phone's notes app or an online document. The addresses remain visible, but at least the device itself requires authentication to unlock.
When adding accounts to Watch Mode, verify each address or xpub through an independent channel. If importing an exchange deposit address, confirm it through a withdrawal email or the account settings page accessed directly (not through a link in email). If importing an xpub from a hardware wallet, derive it from the device using the hardware wallet's application rather than copying it from a recovery phrase or previous export. This prevents typos and reduces the risk of adding a wrong address that could feed false data into the portfolio view.
Periodic review of the accounts listed in Watch Mode is also advisable. As custody arrangements change—an exchange account is closed, a staking service is replaced, or assets are consolidated—the Watch Mode accounts should be removed to keep the interface current and prevent confusion. A stale address that was previously used but is no longer active creates unnecessary clutter and could lead to mistakes if forgotten context is later rediscovered.
When Watch Mode is insufficient and full application functionality is needed
Watch Mode is designed for observation, not transaction initiation. If a user intends to send assets, stake holdings, swap tokens, or interact with DeFi contracts, those actions require a device with private key access. Ledger Wallet's full functionality—including the ability to install blockchain applications, manage staking through compatible protocols, and execute swaps—is available only when a Ledger hardware device is connected. Users attempting to sign transactions from Watch Mode will be prompted to connect a hardware device or use an alternative signing mechanism, depending on the asset and action.
This separation is by design. It enforces the boundary between monitoring and acting, reducing the likelihood of casual mistakes. However, it also means that Watch Mode alone cannot serve as a complete portfolio management tool for active traders or users who frequently execute transactions. The design is optimized for buy-and-hold strategies, staking management, and passive observation, not for frequent rebalancing or complex transaction execution.
Users requiring both unified monitoring and frequent trading might consider maintaining Watch Mode for portfolio observation while keeping separate signing applications for execution. This requires discipline to avoid confusion about which application manages which accounts, but it provides both the convenience of centralized tracking and the control of distributed custody. The alternative—using Ledger Watch Mode as a monitoring layer and separate applications for each custody provider—accepts less integration in exchange for better specialization.
The strategic value of unified observation without unified custody
The original appeal of consolidating crypto assets into a single exchange or custodian is simplicity: one login, one interface, one place to track and manage everything. The security cost of that simplicity is a single point of failure. Exchange insolvency, regulatory action, account takeover, or technical failure can affect all holdings at once. Distributed custody avoids that concentrated risk but introduces the operational burden of managing multiple interfaces and remembering separate details for each account.
Watch Mode bridges that gap by providing unified observation without unified custody. A user can maintain assets across multiple self-custodied wallets, hardware devices, staking services, and exchanges while viewing them all from a single consolidated interface. The operational ease of a unified dashboard is recovered without the security cost of moving assets to a single location. This model works particularly well for longer-term holdings, diversified strategies, and users who can tolerate the slight friction of switching applications when they do need to execute transactions.
For power users managing substantial portfolios, this approach becomes increasingly valuable. The ability to see the complete picture—how much is in hardware wallets, how much is staked, how much is on exchanges for trading, how much is deployed in DeFi—informs better decision-making about rebalancing, risk management, and capital allocation. Ledger Watch Mode makes that comprehensive view achievable without requiring the underlying assets to be consolidated into a single account or service.
The watch-only model also scales naturally. As a user's portfolio grows and custody arrangements become more complex, adding new accounts to Watch Mode is trivial, whereas consolidating everything into a single interface would require repeated migrations and increasing reliance on a single provider. The discipline of maintaining separated custody is reinforced rather than undermined by using a unified monitoring tool.
Frequently asked questions
Can I send cryptocurrency using Ledger Watch Mode?
No. Watch Mode is read-only and displays balances and transaction history without signing capability. To send assets, you must use the application or device where the private key is stored. This separation is intentional—it prevents accidental transactions while maintaining portfolio visibility on any internet-connected device.
Is it safe to add my bitcoin xpub or Ethereum address to Watch Mode?
Adding a public key or address to Watch Mode does not expose your private key or put your funds at risk of being moved by others. The public key is already recorded on the blockchain when you transact. Watch Mode adds a small network metadata risk if an observer can correlate queries, but the benefit of unified portfolio tracking typically outweighs this for most users. Verify addresses through independent channels to prevent typing errors.
What blockchains and assets does Ledger Watch Mode support?
Ledger Wallet supports major blockchains including Bitcoin, Ethereum, Solana, Litecoin, Cardano, and Polygon, among others. Support varies by asset type; not every token or Layer 2 network is available. Before designing a portfolio tracking workflow around Watch Mode, verify that your intended blockchains and assets are supported or plan alternative solutions for unsupported holdings.
Why Liquidity Provision and Market Making Decide Which DEX Professionals Use for Perpetuals
“High liquidity” is a phrase that persuades many marketing decks, but a useful mental model for a professional trader is more precise: liquidity quality is depth × resilience × speed. A platform can display deep bids and asks on a snapshot, and still be fragile when a large order, coordinated flows, or an oracle shock arrives. For US-based professional traders who need tight spreads, low slippage, and predictable execution on perpetual futures, understanding the mechanics that create (and break) on-chain liquidity is the difference between strategy edge and surprise losses.
This explainer walks through how liquidity is created on decentralized perpetuals, how modern DEXs blend order books and liquidity pools to solve different problems, and where trade-offs — from centralization to tokenomics — change what you should expect at the desk. I use the recent operational design and news around Hyperliquid as a running example to show concrete mechanisms, practical limits, and signal events to watch next week and next quarter.

Mechanics: How on-chain market making for perpetuals actually works
Perpetual futures are synthetic contracts that track an underlying price without settlement dates. Two liquidity mechanisms are common on-chain: central limit order books (CLOBs) and automated market makers (AMMs). CLOBs let professional traders post discrete limit orders and express directional convictions; AMMs provide continuous curves that make instantaneous matching easy. A hybrid — an on-chain CLOB supplemented by a community-owned liquidity vault — combines the precision of limit orders with the spread-tightening effect of pooled capital.
Key components that implement this in practice: (1) order routing and matching speed, (2) a liquidity backstop to absorb large market orders, (3) robust margin and liquidation mechanics, and (4) mechanism design that discourages manipulative round-trips. Execution speed matters because latency converts to cost when high-frequency actors arbitrage small price differences. On a bespoke Layer‑1 optimized for trading, sub-second block times and absorbed gas costs materially lower the all-in trading friction.
Hyperliquid’s architecture illustrates these mechanics: it runs an on-chain CLOB for professional order types (TWAP, scaled orders, stop-loss, etc.), while the Hyper Liquidity Provider (HLP) Vault acts as an AMM-style backstop that tightens spreads. The chain’s design — HyperEVM with HyperBFT consensus and ~0.07s block times — is explicitly tuned to reduce execution slippage for aggressive order flow and to let advanced order management function smoothly without network congestion.
Why hybrid liquidity is attractive — and where it breaks
Hybrid models reduce the classic trade-off between tight spreads and continuous depth. Limit orders provide depth at the displayed prices; a vault supplies hidden depth and can absorb sweeps. For a pro trader, that means smaller market-impact costs on both entry and exit and more predictable performance for levered perpetuals up to 50x. When the platform waives user-level gas, friction falls further: the only recurring cost becomes maker/taker fees, which are easier to price into an algo or a PnL model.
However, the hybrid model creates new failure modes. First, vaults depend on predictable fee and liquidation revenue to remain solvent; extreme tail events — sudden multi-asset deleveraging or oracle divergence — can deplete vault reserves and widen spreads. Second, centralized trade-offs enter the picture: achieving sub-second latency often requires fewer validators and more trusted infrastructure. That design increases the risk vector in governance or validator misbehavior compared with widely distributed L1s. For market makers, this is a risk-premium decision: lower slippage today, systemic counterparty or operational risk tomorrow.
Another practical limit is the platform’s ability to prevent manipulation on low-liquidity alt markets. Recent operational history shows that low-liquidity pools are attractive targets for quote-stuffing, spoofing, and wash-like flows when strict automated position limits and circuit breakers are absent. A market that allows large, unchecked positions without robust automated checks can produce flash squeezes that harm liquidity providers and traders alike.
Clearing, margin, and the non-custodial model — advantages and frictions
Non-custodial exchanges change the legal and operational calculus for pro desks: traders keep control of private keys and collateral, and liquidations are enforced by decentralized clearinghouses. This removes settlement counterparty risk inherent in centralized exchanges, but it raises engineering constraints. Liquidations must be rapid and well-incentivized; otherwise, undercollateralized positions can create insolvency cascades. When margin enforcement is decentralized, the quality of the liquidation mechanism (speed, auction design, and participation incentives) becomes an axis of liquidity health.
Cross-margin vs. isolated margin choices affect both portfolio management and pool stability. Cross-margin improves capital efficiency — useful for institutional flows such as Ripple Prime’s recent integration that routes over 300 clients into cross-margin perpetuals — but it increases contagion risk if one position deteriorates sharply. Isolated margin limits that contagion but forces higher capital usage. For firms optimizing capital utilization, the trade-off between resilience and efficiency is central.
Tokenomics, treasury moves, and liquidity incentives
Native tokens and treasury strategies can enhance liquidity if they align incentives correctly. A fixed-supply governance token used for staking and fee distributions concentrates long-term incentives with early adopters; that can bootstrap deep liquidity provision if early holders stake into vaults or act as market makers. But token unlocks and treasury collateralization strategies matter materially.
For example, a recent scheduled release of nearly 9.92 million HYPE tokens — a notable supply unlock — created a short-window market pressure event that liquidity providers had to absorb. Separately, the treasury’s use of 1.86 million HYPE as options collateral to generate yield is a sophisticated approach to monetize reserves, but it also ties treasury solvency to option market behaviour. These moves are neither uniformly positive nor negative; they change the supply-demand dynamics that underpin both passive liquidity in vaults and active quoting by market makers.
Practical implication: when reviewing a DEX, watch token unlock schedules, treasury hedging strategies, and any publicized institutional integrations. Each alters the expected fee revenue and tail-risk exposure for liquidity providers.
Comparative heuristics: when to prefer a hybrid on-chain CLOB + vault vs other designs
Here are decision-useful heuristics that pro traders can reuse when selecting a venue for perpetuals:
- Choose hybrid CLOB + vault when you need advanced order types, low displayed spreads, and reliable sub-second execution for high-frequency or algorithmic strategies.
- Choose pure AMM-based venues when you accept larger structural spreads but want simplicity and passive exposure without running a market-making engine.
- Prefer venues with robust automated circuit breakers and position limits for trading low-liquidity alt contracts; the absence of those controls materially raises manipulation risk.
- If capital efficiency is your priority, prefer platforms that support cross-margin and have deep institutional flow integrations — but stress-test their liquidation rules.
Hyperliquid’s combination of an on-chain CLOB, the HLP Vault, advanced order management, and a bespoke high-speed L1 positions it where the first heuristic applies. The network’s centralization trade-off (a limited validator set) and recent HYPE token unlocks are the kind of operational signals you should factor into risk models.
Where this design is likely to evolve and what to monitor next
Three signals will indicate whether these hybrid, high-speed DEX designs converge toward reliable venues for professional US-based traders or revert toward niche use:
- Protocol-level circuit breakers and automated position limits: adoption of stricter, transparent rules reduces manipulation risk and improves institutional uptake.
- Validator decentralization roadmap: a plan (and measurable progress) to increase validator diversity reduces centralization premium and regulatory optics.
- Treasury and token-supply management: predictable and market-aware unlock schedules and hedging strategies lower tail risk for liquidity providers.
Operational news in early February shows activity on these fronts: institutional integration with Ripple Prime opens a reliable channel of professional order flow, while large token unlocks and treasury hedging via options increase the near-term volatility the network must absorb. These are not contradictory: institutional flow can stabilize order books if the infrastructure handles spiky events and if vault economics remain intact.
For traders in the US, regulatory and counterparty perception also matter. Non-custodial designs reduce custody concerns, but centralization choices and the behavior of token distributions will remain part of enterprise due diligence.
FAQ
How does a hybrid on-chain order book plus vault reduce slippage compared with a pure AMM?
Limit orders in an order book show depth at discrete prices, enabling large taker trades to execute against posted liquidity rather than consuming an entire bonding curve. The vault supplies supplemental liquidity when the order book thins, narrowing spreads during routine flow and absorbing temporary imbalances. The hybrid reduces average slippage but adds dependency on the vault’s capital and fee-income model; if vault reserves are stressed, slippage can widen quickly.
Is non-custodial always safer than centralized custody for professional traders?
Non-custodial models remove a class of counterparty risk (exchange insolvency, withdrawal freezes), but they introduce other operational demands: wallet security, on-chain execution risks, and exposure to auction timing. Also, non-custodial systems rely on the efficacy of decentralized clearing and liquidation mechanisms; deficiencies there can create market risks that traders must manage or hedge.
What specific events should I monitor to assess short-term liquidity risk on a DEX?
Track token unlock schedules, treasury hedging announcements, major institutional integrations, oracle or index provider changes, and any incidents of manipulation or liquidation cascades. Each can cause transient or sustained changes in the depth and resilience of order books.
How do validator centralization and zero-gas trading interact from a risk perspective?
Zero-gas reduces trading friction and is attractive to pro desks; however, achieving it often requires centralized fee absorption and fast consensus, which can mean fewer validators. That accelerates execution but compresses decentralization guarantees. The trade-off is explicit: better latency and cost at the price of higher systemic centralization risk.
Decision-useful takeaway: treat liquidity as a system property, not a snapshot metric. Ask how depth is funded (who supplies capital and why), how the system responds under stress (liquidations, circuit breakers), and what governance or token events can shift incentives overnight. If you want to explore a specific implementation that combines a CLOB, an HLP-style vault, advanced order types, and a high-performance L1, look closely at the operational signals — token unlocks, treasury strategies, and institutional integrations — and weigh them against validator centralization and market-manipulation history before allocating capital.
For traders who want to examine how one such hybrid exchange combines these elements in practice, the project provides documentation and a public interface that summarize their architecture and incentives; you can review their materials here: hyperliquid.
Rabby Wallet for Tax Compliance: Tracking Multi-Wallet Transactions Across Mobile and Desktop
A cryptocurrency holder manages assets across multiple devices and platforms: Ledger hardware for cold storage, MetaMask Mobile on an iPhone for occasional trades, Trust Wallet for staking, and a desktop portfolio tracker used irregularly. When tax time arrives, assembling a complete transaction history becomes a practical nightmare. Records are scattered across five applications, each with its own export format and potential gaps. The accountant receives incomplete CSVs, manual spreadsheets full of typos, and spreadsheets missing entire transaction categories such as internal transfers, yield events, and gas fee refunds. Rabby Wallet's architecture—built to consolidate multiple account sources into a single interface—can meaningfully reduce that friction, provided users understand how the wallet's multi-account model actually functions and what still requires manual reconciliation.
The critical insight is that a wallet managing accounts from different sources does not automatically solve tax reporting; it solves visibility and partial aggregation. Rabby can ingest hardware wallets, mobile wallet integrations, and imported MetaMask accounts, displaying balances and transaction history from those sources in one place. That consolidation is not trivial for tax purposes: when a user can see all transactions in a timeline, duplicate entries become visible, sequence matters, and missing pieces become obvious. However, the wallet's role is to present transaction data accurately to the user, not to generate compliant tax reports. The responsibility for completeness, classification, and filing remains with the account holder and their tax advisor. Understanding that boundary determines whether Rabby becomes a reliable starting point for accurate reporting or remains another source of partial information.
How Rabby's multi-account architecture supports transaction consolidation
Rabby Wallet allows a single user to create, import, and manage multiple accounts using different methods: seed phrases, private keys, hardware wallets, and mobile wallet integrations. This design is fundamentally different from a single-account wallet. Rather than forcing a user to choose one authentication method, Rabby presents an account selection interface where users can switch between an imported MetaMask account, a Ledger device, a native seed-phrase account, and a Trust Wallet connection, all within the same application and browser session.
From a tax perspective, this multi-account capability serves a primary function: it eliminates the operational need to log into five separate applications to find a transaction record or confirm a balance. A user or accountant can open Rabby, select all relevant accounts from the sidebar or account menu, and review transactions across those accounts in sequence. This is not full historical aggregation—Rabby displays transaction history based on what the blockchain records and what the connected wallets expose—but it is a significant step toward completeness. Each connected account, whether from a hardware wallet, mobile integration, or imported private key, can contribute its transaction history to the user's view.
The wallet supports hardware wallet integration with Ledger, Trezor, GridPlus, OneKey, Keystone, BitBox02, and CoolWallet. For a user managing an ice-cold hardware wallet on Ledger and also trading on mobile through MetaMask Mobile, Rabby can show both transaction histories together. The hardware wallet maintains private key isolation on the device, while Rabby acts as the interface to view and sign transactions. The mobile integrations—including MetaMask Mobile, Trust Wallet, TokenPocket, imToken, Math Wallet, Rainbow, Bitget Wallet, and Zerion—can be connected through WalletConnect or direct import, allowing Rabby to read transaction histories from those applications without requiring the user to re-enter private keys or seed phrases.
Watch-only address functionality is equally important for tax tracking. A user may hold funds in addresses that do not reside in any wallet the user directly controls—perhaps a business account, an exchange deposit address monitored for tax purposes, or a multisig arrangement. Adding those addresses as watch-only allows Rabby to monitor their activity without requiring key material. For a business or high-volume trader, being able to see every relevant address's transactions from a single interface is foundational to accurate reporting.
The practical limits of imported accounts and transaction history
Importing a MetaMask account into Rabby by entering the seed phrase or private key does not magically create a complete transaction history. Rabby will display transactions that the blockchain recorded and that its indexing service can access. If a user switched MetaMask to a different recovery phrase two years ago without exporting the transaction history first, the old account's records may no longer be visible in MetaMask, and importing the old seed phrase into Rabby will show only the blockchain transactions associated with that address. Some transactions—especially if they involved older or less common protocols—may not be indexed or may appear with incomplete metadata such as missing labels or incorrect value attribution.
The same limitation applies to Rabby Wallet mobile app connection scenarios. If a user connects Trust Wallet through WalletConnect or imports the seed phrase, Rabby can see transactions Trust Wallet recognizes, but only for addresses and chains that Trust Wallet indexed. If the user previously used a different wallet application—say, an older version of a mobile wallet that is no longer maintained—and then imported the same seed phrase into Trust Wallet, the transaction history visible in Rabby is bounded by what Trust Wallet can retrieve. Historical blockchain data is immutable and publicly available, but Rabby's presentation of that data is limited by the indexing service's coverage and speed.
Institutional wallet integrations add another layer. Rabby supports Safe multisig wallets, Cobo custody solutions, Argus, Amber, Fireblocks, Jade Wallet, and MPCVault. When a user adds a Safe account, they are typically adding a watch-only address and relying on the multisig contract's transaction log. Fireblocks and Cobo transactions may require exports from those platforms to match Rabby's view. Multi-signature or custody transactions often have timing discrepancies: the blockchain records a transaction when it is signed and broadcast, but the custody platform may record it when it was submitted for approval or when it was finally executed. Tax accountants must reconcile those timing differences, and no wallet interface can automatically resolve them.
Rabby's value in these scenarios is not perfect historical coverage; it is clarity about what is missing. A user who checks five separate wallets and assembles a manual list may not notice a gap. A user who imports all accounts into Rabby and reviews transactions in chronological order can more easily spot the year when activity is sparse, the chain where no transactions appear, or the address that has been forgotten. That negative space is easier to see in an aggregated view than in separate applications.
Contact management and manual record keeping for tax documentation
Rabby includes contact functionality, allowing users to save labels for frequently used addresses. This is a tax-preparation tool, not a privacy feature. When a user sends funds to an exchange deposit address, a multisig participant address, or a service provider address repeatedly, labeling that contact in Rabby makes the connection explicit. An accountant reviewing the transaction history can immediately see that address X is "Kraken deposit," and address Y is "Tax professional's wallet." This prevents misclassification and makes it obvious when an account has received transfers from unrelated sources.
However, contact management does not replace written documentation. Tax authorities, especially those in jurisdictions with detailed reporting requirements, often require contemporaneous documentation: records of the transaction date, the counterparty, the business purpose, the consideration received, and the method of valuation. Rabby shows the transaction on-chain, but it cannot capture the reason why a transaction occurred. A transfer to an address labeled "USD stablecoin sale" must be paired with records of when those stablecoins were acquired, at what price, and whether the sale proceeds went to a bank account or were used to purchase other assets. The wallet is one input to that documentation; it is not the complete record.
Users preparing for tax season should therefore treat Rabby as a discovery tool first and a record source second. Export the transaction history from Rabby in a standard format—CSV is common—and then cross-check it against bank records, exchange deposit addresses, and any manual trades executed outside of tracked wallets. This process will identify duplicates, missing pieces, and inconsistencies. If a bank deposit matches a blockchain transaction, the link should be documented. If a transaction history gap exists, that gap should be investigated before reporting.
Coordinating desktop and mobile wallet activity in one reporting timeline
Many high-volume cryptocurrency users maintain a split workflow: cold storage and long-term holdings on a hardware wallet connected to a desktop application, and active trading or frequent transactions on mobile through a separate wallet. Rabby unifies that split by allowing both to be viewed together. A user with a Ledger device managed through Rabby on desktop can also connect a Trust Wallet or MetaMask Mobile through WalletConnect, seeing both the infrequent hardware transactions and the frequent mobile trades in a single transaction list.
For tax reporting, this unification exposes patterns that would otherwise be fragmented across two reports. If a user swaps tokens on mobile weekly and stakes assets on hardware monthly, those two transaction types can appear in their chronological sequence. That context matters for understanding the user's trading pattern and portfolio management. It also matters for cost basis tracking: if a user buys tokens on an exchange, receives them in a mobile wallet, and then transfers them to cold storage, the cost basis should follow that token through all three events. A unified timeline makes the flow of assets easier to trace.
The downside is that unifying timelines also exposes discrepancies. A user who thought they made only occasional trades may be startled to see transaction frequency across mobile wallets they use casually. A trader who imported multiple mobile wallets may discover duplicates if the same trade is executed simultaneously on two platforms or if the same wallet was imported twice. These discrepancies are real problems that a separate-wallet approach would have hidden. The solution is to review the unified history carefully, identify any duplicate entries or unexplained gaps, and resolve them before export. This is more work in the moment but prevents larger errors later.
Institutional and custodial account compliance reporting
Organizations and high-net-worth individuals often use institutional custody services such as Fireblocks, Cobo, or Amber for on-chain asset management, combined with multisig solutions like Safe. Rabby's integration with these platforms means that an organization's accountant can potentially see all on-chain activity—cold storage through hardware wallets, hot wallets through mobile integrations, and custody-managed assets through institutional connections—in one interface.
The practical value for compliance is that it becomes possible to verify that custody platform records match the blockchain. If Fireblocks shows a transaction as executed on a given date and time, that transaction should be visible on-chain with the same timestamp. If there is a discrepancy, it must be investigated before filing. Rabby cannot directly resolve custody records into tax lots—that requires mapping the transaction to the order that triggered it—but it can confirm that the transaction did occur and associate it with the correct wallet or smart contract address.
For organizations using multisig arrangements such as Safe, Rabby displays the multisig contract's transactions, but it shows them from the perspective of the blockchain. A Safe transaction involves multiple signers and an execution event; the blockchain records the execution, but the Safe interface shows the approval history. A tax accountant must understand this distinction: the transaction date for tax purposes is typically the blockchain confirmation date, not the date when a transaction was signed or when the execution was initiated. Rabby's transaction list will show the confirmation date, aligning it with how tax authorities typically interpret blockchain records.
Exporting transaction data and integrating with tax software
Rabby allows users to export transaction histories in formats suitable for tax software integration. A CSV export from Rabby will include transaction dates, amounts, asset types, counterparty addresses, and transaction hashes. This export is a starting point, not a complete tax report. Tax software such as Koinly, CryptoTrader.Tax, or ZenLedger can ingest the CSV and attempt to automatically classify transactions into income, capital gains, transfers, and so forth. The software's accuracy depends on how complete the export is, how clear the transaction labels are, and how well the software's classification rules match the jurisdiction's requirements.
A common error is uploading a Rabby export to tax software without verifying that all transactions are present. If the export covers only Ethereum and Polygon transactions but the user also traded on Bitcoin, the export is incomplete. If the export begins midway through a calendar year, income from earlier transactions will be missing. The user's responsibility is to ensure that the export captures every transaction on every chain that the user participated in during the tax year. Rabby can facilitate that verification by allowing the user to select specific date ranges and chains, creating separate exports to make sure nothing is missed.
Some jurisdictions require detailed documentation of gas fees, yield events, and internal transfers. Rabby transaction exports typically include these events, but their classification in tax software varies. A transfer between two wallets the user owns is not typically a taxable event in most jurisdictions, but it is a transfer of basis. Gas fees are usually deductible as transaction costs, but only if the user can associate them with a specific taxable transaction. The accountant must review the raw transaction data and adjust classifications that the software has applied incorrectly.
Best practices for maintaining accurate records throughout the year
Rather than scrambling to export and verify transactions at tax time, users should maintain records continuously. Creating a simple spreadsheet that tracks major transactions as they occur—the date, asset, amount, counterparty or exchange, and business purpose—provides a paper trail that can be quickly cross-checked against Rabby's exported history. When discrepancies appear, they are easier to resolve while the context is fresh.
Users should also perform regular audits of their wallet configuration. Every quarter or semi-annually, verify that all accounts are still connected to Rabby, that no accounts have been deleted or forgotten, and that the transaction history is current. If a user creates a new wallet and forgets to add it to Rabby, that account's transactions will not be included in the year-end export. Similarly, if a user changes their seed phrase or rotates to a new hardware wallet, the old wallet must remain accessible in Rabby if its historical transactions are needed for tax purposes.
For users with complex transactions—staking rewards, yield farming, DeFi interactions, or NFT sales—Rabby may not classify every event correctly. A liquidity pool deposit that mints an LP token is not simply a transfer; it is a trade of one asset for a position token. A staking reward is income, and its value should be recorded at the moment it was received, not at the moment it was sold. These nuances require either software that understands the specific protocol or manual accounting. Rabby provides the raw data; the user or their accountant must interpret it correctly for tax purposes.
Comparing Rabby's consolidation to standalone platform exports
An alternative to using Rabby is to export transaction histories directly from each platform: MetaMask, Trust Wallet, Ledger Live, Fireblocks, Cobo, and so forth. This approach is more tedious but avoids introducing an intermediary. The user manually combines exports into one spreadsheet or uploads them sequentially to tax software. The downside is that manual combination is error-prone, and gaps become less obvious when records are not presented in chronological sequence.
Using Rabby reduces that manual labor. Instead of exporting from five separate applications and stitching them together, the user exports once from Rabby and receives a unified list. Duplicates are visible because transactions appear in sequence. Gaps are obvious because an address's activity can be compared across all connected accounts. The cryptocurrency management benefit is not just convenience; it is accuracy. A consolidated view is easier to audit than fragmented records.
However, this advantage comes with a risk: relying too heavily on a single interface can create false confidence in completeness. If Rabby fails to display a transaction—perhaps because the indexing service has a bug, or a specific token is not recognized—the user may export an incomplete history without realizing it. This is why the verification step is critical. The user must periodically compare a Rabby export against independent records, such as blockchain explorers, exchange statements, and bank deposits, to ensure nothing is missing.
Frequently asked questions
Can Rabby Wallet automatically generate a tax-compliant report?
No. Rabby consolidates transaction data from multiple wallets and accounts, making that data available for export and review. It does not classify transactions, assign cost basis, or determine tax liability. Users must export their transaction history, verify completeness, and work with tax software or an accountant to classify transactions according to their jurisdiction's rules and their individual circumstances.
If I import a MetaMask account into Rabby, will I see all historical transactions?
Rabby will display transactions that the blockchain records for that account's addresses, subject to the limitations of its indexing service. If MetaMask previously displayed a transaction but it is not indexed in Rabby's system, it may not appear. You should always cross-check Rabby's export against your own records, blockchain explorers, and other sources to ensure completeness before submitting tax reports.
How should I handle staking rewards and DeFi transactions for tax purposes?
Rabby will display these transactions on-chain, but it may not classify them correctly for tax purposes. Staking rewards are typically income at the moment of receipt; DeFi interactions such as liquidity pool deposits involve trades of assets for position tokens. Your accountant or tax software must review these transactions manually and assign the correct classification. Rabby provides the data; you provide the interpretation.
Cryptocurrency Wallet Fingerprinting Through Transaction Propagation Timing: Can XMRWallet Users Be De-Anonymized by Network Observers?
Monero's cryptographic architecture hides transaction amounts, sender addresses, and receiver addresses from the public blockchain. Yet a user running XMRWallet and broadcasting a transaction to the network creates a moment of visibility that cryptography does not control: the broadcast itself. An observer positioned on the network path between a user's device and a Monero node can record when a transaction appears, from which direction it arrives, and how long it takes to propagate. That metadata layer exists independent of whether Monero's ring signatures, stealth addresses, or RingCT obscure the transaction's financial content. The question is whether this timing and network pattern can be used to link a user's identity to their cryptocurrency activity, regardless of Monero's on-chain privacy.
This threat is neither theoretical nor negligible for a typical XMRWallet user. The wallet's non-custodial architecture, which reconstructs cryptographic keys locally without storing sensitive data on servers, solves the problem of service-provider custody risk. However, it does not solve the problem of network observation. When a user logs in using an encrypted wallet file with password or a 25-word recovery seed and then broadcasts a transaction, the timing, frequency, and pattern of network activity can create an observable fingerprint. Internet service providers, network administrators, VPN providers, and state-level actors can all observe packet flows at different network layers. The practical question for users is whether these observations can be used to defeat Monero's privacy guarantees, and which design choices in wallet software can reduce the risk.

The distinction between ledger privacy and network privacy
Monero achieves ledger privacy through ring signatures, which mix a real transaction input with decoys; stealth addresses, which create unique addresses for each received payment; and RingCT, which hides transaction amounts. An observer with access to the full blockchain cannot determine which address sent funds, which address received them, or what amount moved. This is a fundamental cryptographic property that remains true regardless of network observation.
Network privacy is different. It concerns what an observer can infer from traffic patterns, timing, and connection metadata. When a user's device connects to a Monero node and submits a transaction, several pieces of information become observable: the approximate time of the broadcast, the source IP address (if no proxy is used), the packet size and shape, the destination node's address, and the frequency and timing of similar broadcasts from the same source. None of this information appears on the blockchain, but an observer positioned appropriately on the network path can collect it.
The two privacy layers can fail independently. A user with Monero's strongest ledger privacy guarantees might still broadcast a transaction in a way that immediately ties it to their IP address and device. Conversely, a user communicating through multiple proxies might have strong network privacy yet accidentally reveal transaction patterns through timing or behavioral habits. The practical privacy outcome depends on both layers together. A user who achieves network anonymity but is later identified through conventional investigation (a subpoena, a warrant, a leak, or an informant) is no better off; the leaked identity can then be linked retroactively to the anonymous transaction broadcasts.
XMRWallet's architecture does not inherently address the network layer. The wallet is non-custodial, meaning no passwords or recovery seeds are stored server-side and the user maintains full responsibility for security. However, a user must still connect to a Monero node to scan the blockchain, derive balances, and broadcast transactions. That connection is where network observation can occur.
How transaction broadcast timing reveals patterns
When a user broadcasts a transaction, the propagation across the Monero peer-to-peer network is not instantaneous. The transaction starts at the node that first receives it, then spreads to neighboring nodes, then to their neighbors, in a wave pattern. Researchers have shown that an observer monitoring enough nodes in the network can trace this propagation backward to estimate the origin node. If an observer can further correlate the timing of a transaction's appearance with the activity on an IP address or a known VPN exit node, they can narrow the suspect pool dramatically.
The first peer that receives a transaction is the most revealing data point. If a user always broadcasts through the same Monero node, and an observer can monitor that node's incoming connections, they can observe which source IPs submit transactions and at what times. The timing information is particularly useful because human behavior is predictable. A user who generates a transaction between 9 and 10 AM on weekdays is narrower set than a truly random time. Similarly, a user whose transaction broadcasts always occur with a 30-second gap after they click "send" in the UI is exhibiting a timing signature that could eventually be correlated with known individuals or activity patterns.
The risk escalates if a user connects directly to a remote node without a proxy. An observer at the ISP level, or a network administrator at the user's workplace or home, can see the IP address initiating the connection and the timing of packets flowing to the Monero node. If the user's IP address is already associated with their identity (through a home internet account, a workplace, or a VPN that maintains logs), the connection alone becomes incriminating. The observer does not need to decode the transaction or learn which address sent funds; they only need to prove that the user's device was communicating with Monero infrastructure at the moment a specific transaction appeared.
The remote node decision and its privacy implications
XMRWallet allows users to connect to either a local Monero node running on the same device or a remote node operated elsewhere. This design choice has profound privacy consequences. A local node handles all blockchain synchronization and transaction scanning on the user's device, keeping network traffic associated with Monero activity confined to the device itself. A remote node means the user sends queries to an external server, revealing which addresses the wallet is interested in monitoring.
From a network fingerprinting perspective, a remote node creates an additional risk. The remote node operator, or an observer between the user and the remote node, can see which addresses the wallet is querying. Monero's view-key architecture allows a user to prove they received a transaction to someone without revealing the spending key, but a remote node query pattern still creates behavioral information. If a user always queries the same address at 11 AM on Tuesdays, the remote node operator could begin to anticipate activity and correlate it with external events, payments, or employment schedules.
However, a local node is not costless. Running a full Monero node requires significant bandwidth and storage, and not all users have the resources to maintain one continuously. A compromise is available: using a remote node while tunneling the connection through Tor or a VPN. This does not eliminate the remote node's ability to see address queries, but it does prevent the remote node from learning the user's IP address. If the user alternates among several remote nodes, or uses a privacy-focused node service that explicitly does not log queries, the risk is further reduced. The key is understanding that each choice trades off convenience against a different aspect of network privacy.
Blockchain synchronization as a timing oracle
When an XMRWallet user first accesses their wallet or reconnects after being offline, the wallet must synchronize with the blockchain to know the current state and detect new received transactions. This synchronization is observable. The user's device contacts a node (local or remote) and retrieves blocks, sending queries in a specific pattern. If the wallet scans blocks sequentially from a known height, an observer can infer how long the user has been offline and when they resumed activity.
More subtly, the synchronization process creates a distinctive timing pattern. A user opening XMRWallet for the first time in a day will trigger a burst of blockchain queries. An observer watching that node's incoming traffic can see the pattern repeated daily, roughly at the same times. This becomes a behavioral signature. If the synchronization also includes address index lookups or specific query patterns designed to search for received payments, the traffic shape becomes even more distinctive. A machine-learning classifier trained on enough examples might eventually distinguish between different users' wallets based solely on their synchronization patterns.
The Monero protocol addresses some of this through compacted block information and filtered block downloads, which reduce the data transmitted. However, even compressed synchronization is observable in terms of frequency and timing. A user who syncs every ten minutes is exhibiting different behavior from one who syncs once daily. Neither behavior is inherently private just because the block data is encrypted in transit or queried from a local node.
The practical role of proxying and tunneling
The most straightforward defense against network-level IP address identification is to use a proxy or a VPN between the XMRWallet login process and the Monero node. Tor is the strongest option because it routes traffic through multiple relays, making it difficult for a single observer to correlate source and destination. A commercial VPN service provides a weaker guarantee—the VPN provider sees the user's real IP address—but it obscures the user's identity from the Monero node and from passive observers on the network path.
However, proxying introduces its own risks. A VPN provider with inadequate logging policies can later be compelled to produce records of user activity. A Tor exit node, while anonymizing the source, can be operated by an adversary who observes all traffic exiting to the Monero network. If the adversary controls multiple exit nodes or can observe traffic from the user's ISP to the Tor network, they can perform correlation attacks across the Tor circuit. The standard advice to use Tor is sound, but it should not be mistaken for complete network anonymity; it is a significant defense against casual observation and passive ISP-level surveillance.
The wallet software itself can support better proxying practices. If XMRWallet were to require users to specify a proxy, or to route all connections through Tor by default, the fingerprinting risk would decline substantially. However, the wallet's design emphasizes flexibility, allowing users to connect directly to a remote node, to configure a local node, or to use external services. This flexibility is valuable for users who understand the trade-offs, but it also creates a footgun: a user can unknowingly connect directly to a node and broadcast transactions with their IP address exposed.
Temporal correlation attacks and behavioral clustering
A sophisticated attacker does not need to observe every transaction. They can use statistical techniques to link multiple transactions together based on timing alone. If a Monero observer collects timestamps of all transactions broadcast by a particular IP address or Tor exit node over weeks or months, they can build a pattern. The attacker then correlates this pattern with external evidence: when does this cluster of transactions occur relative to other events? Do transactions spike at lunch time, suggesting a merchant processing orders? Do they occur in precise increments, suggesting automatic payments? Do they cluster around specific calendar dates, suggesting salary payments or bill cycles?
This approach is powerful because it does not require breaking Monero's cryptography or even knowing which transactions belong to which address. The attacker is clustering transactions by timing and treating the cluster as a proxy for a user or entity. Once several transactions are clustered together, the attacker can search for external correlations: forum posts, social media activity, email leaks, or other traces that occur at the same time. If a known person's leaked correspondence shows they made a Monero payment at a specific time, and that time matches a transaction broadcast from a particular IP address, the correlation becomes evidence.
Defense against temporal correlation requires either truly random broadcast timing, or deliberate obfuscation. A wallet could add random delays before broadcasting, submit multiple decoy transactions, or batch legitimate transactions with dummy transactions. However, these defenses require careful implementation to avoid creating new patterns. A wallet that always adds 30 seconds of delay creates a different timing signature than a wallet that broadcasts immediately. The question is whether the new signature is harder to link to known individuals.
Node selection and the myth of decentralization
Some Monero users believe that connecting to a remote node is "decentralized" and therefore private, because the node is not controlled by a corporation or a central authority. This is partly true: a small community-operated node is not controlled by a company with financial incentives to log or sell data. However, "decentralized" is not the same as "anonymous." An observer does not care whether a node is run by a nonprofit or a for-profit entity; they only care about the traffic that crosses its connection.
Furthermore, not all remote nodes are equally trustworthy. A Monero user can learn more about connecting to nodes that align with their privacy expectations through learn more resources and community forums, but the responsibility for evaluating node trustworthiness remains with the user. A node operated by an anonymous individual could be run by a researcher, a law enforcement agency, or a private investigator. The node's anonymity provides no assurance of its operator's good faith. A user connecting to an untrusted remote node hands over address queries and broadcast patterns in exchange for convenience.
A better mental model treats remote node selection as a security decision parallel to VPN provider selection. The user should consider: Does the node operator have visibility into my address queries? Can I verify the node's identity and history? Does the node's operator have any institutional incentive to log or sell data? Would I be comfortable if my address queries were correlated with my identity? These questions do not have universal answers; they depend on the user's threat model and resources. However, they reframe "decentralized node" from a privacy guarantee to a design choice with specific advantages and limitations.
Practical risk reduction for XMRWallet users
A user who wants to reduce fingerprinting risk should adopt several habits together, rather than relying on any single technique. First, use Tor or a reputable VPN when accessing XMRWallet and submitting transactions. Configure the wallet to route all connections through the proxy, not just some. Second, vary the time of day and the day of the week when submitting transactions, if the transaction timing is not constrained by external requirements. This reduces the predictability of behavioral patterns. Third, if using a remote node, select one that is operated by a trusted party and verify that the operator has a clear privacy policy regarding query logging.
Fourth, consider batching transactions where possible. If a user needs to send three payments, submitting them in a single batch—rather than as three separate broadcasts hours apart—creates a less informative timing pattern. Fifth, use a local node if the user has the resources. A local node eliminates the remote-node query leakage entirely and keeps blockchain synchronization traffic isolated to the user's device. Sixth, avoid logging into XMRWallet from public devices or networks where other observers might be present. The login process reconstructs cryptographic keys locally, which means an observer with physical or network access to the device at login time could potentially extract keys or monitor the reconstruction.
Finally, understand that perfect network privacy is not achievable without significant operational discipline. A user who logs into XMRWallet through Tor, broadcasts a transaction, and then immediately posts on a forum under their real name has defeated the network anonymity through their own behavior. The network-level privacy protections are tools; they require consistent application across the user's entire operational security practice. A wallet can facilitate better practices by making proxying automatic or enforcing sensible defaults, but the user's choices ultimately determine whether network fingerprinting is a realistic threat.
Future wallet design and protocol-level solutions
The limitations of XMRWallet's current design are not unique to that wallet; they reflect the broader challenge of providing privacy at the network layer while maintaining usability. Future improvements could include built-in Tor support as a default, mandatory proxy routing, traffic padding to obscure the size and timing of transactions, and integration with Monero's dandelion routing protocol, which can delay and obfuscate transaction origin.
At the protocol level, Monero's development community is exploring Kovri, a privacy-focused router that would eventually allow Monero nodes to communicate over anonymized paths instead of clear IP addresses. Once Kovri reaches production, users could connect to Monero nodes through this anonymized network layer, eliminating the need for external proxies. However, Kovri's development timeline is uncertain, and current users cannot rely on future improvements. The decision to use proxies, manage node connections carefully, and adopt careful operational security must be made now with existing tools.
For wallet developers, the most important improvement is transparency about network privacy limitations. A wallet should clearly document which user activities are observable at the network layer, which proxying methods are recommended, and what behavioral patterns create fingerprints. This is less glamorous than advertising cryptographic features, but it is more practically useful. A user who understands that their transaction broadcast timing can be observed and who adopts Tor as a result is better protected than a user who believes the wallet is "fully private" and broadcasts transactions over a direct connection.
Frequently asked questions
Can an observer see my transaction details if I use XMRWallet with Monero's privacy features?
No. Monero's ring signatures, stealth addresses, and RingCT hide sender, receiver, and amount information on the blockchain. An observer cannot determine these details from the ledger itself. However, the same observer can potentially see the timing and network path of your transaction broadcast if you do not use a proxy, revealing your IP address and behavioral patterns even though the transaction's financial content remains private.
Does using a remote node expose my addresses and privacy?
A remote node can see which addresses your wallet queries, which reveals behavioral information about when you check balances and which addresses are associated with your wallet. This is less sensitive than exposing the addresses to the public blockchain, but it is still a privacy leak if the remote node operator is untrustworthy. Using a proxy (Tor or VPN) between your wallet and the remote node prevents the node operator from seeing your IP address, but the operator can still see your address queries unless the wallet implements additional privacy measures.
Should I always use Tor with XMRWallet?
Using Tor is strongly recommended if your threat model includes network-level observation from an ISP, network administrator, or state-level actor. Tor prevents your IP address from being exposed to the Monero node and makes it harder for an observer to correlate your transaction broadcasts with your identity. However, Tor does not eliminate all risks: an adversary controlling Tor exit nodes or observing traffic to the Tor entry nodes might still perform correlation attacks. Combined with good operational security practices—varying transaction timing, using a trustworthy node, and not linking Monero activity to other identifying information—Tor provides substantial protection.
Rabby Wallet vs. Other Web3 Wallets: What DeFi Users Should Actually Compare
What if the most important wallet feature is not how quickly it signs a transaction, but how much it can reveal before you sign? In decentralized finance, a wallet is more than a password-protected address. It is the interface through which users authorize token approvals, interact with smart contracts, bridge assets, provide liquidity, and sometimes expose an entire portfolio to an unfamiliar protocol. A polished interface can make those actions feel routine. The underlying risk is not routine at all.
This is where an advanced wallet such as rabby deserves comparison rather than automatic praise. Its emphasis on transaction simulation, pre-signing risk signals, and DeFi-oriented workflows addresses a real weakness in conventional wallets: users often see a confirmation request without understanding the state change it will cause. Yet no wallet can convert an adversarial or defective smart contract into a safe one. The useful question is therefore not “Which wallet is best?” but “Which wallet’s trade-offs match the decisions I make?”
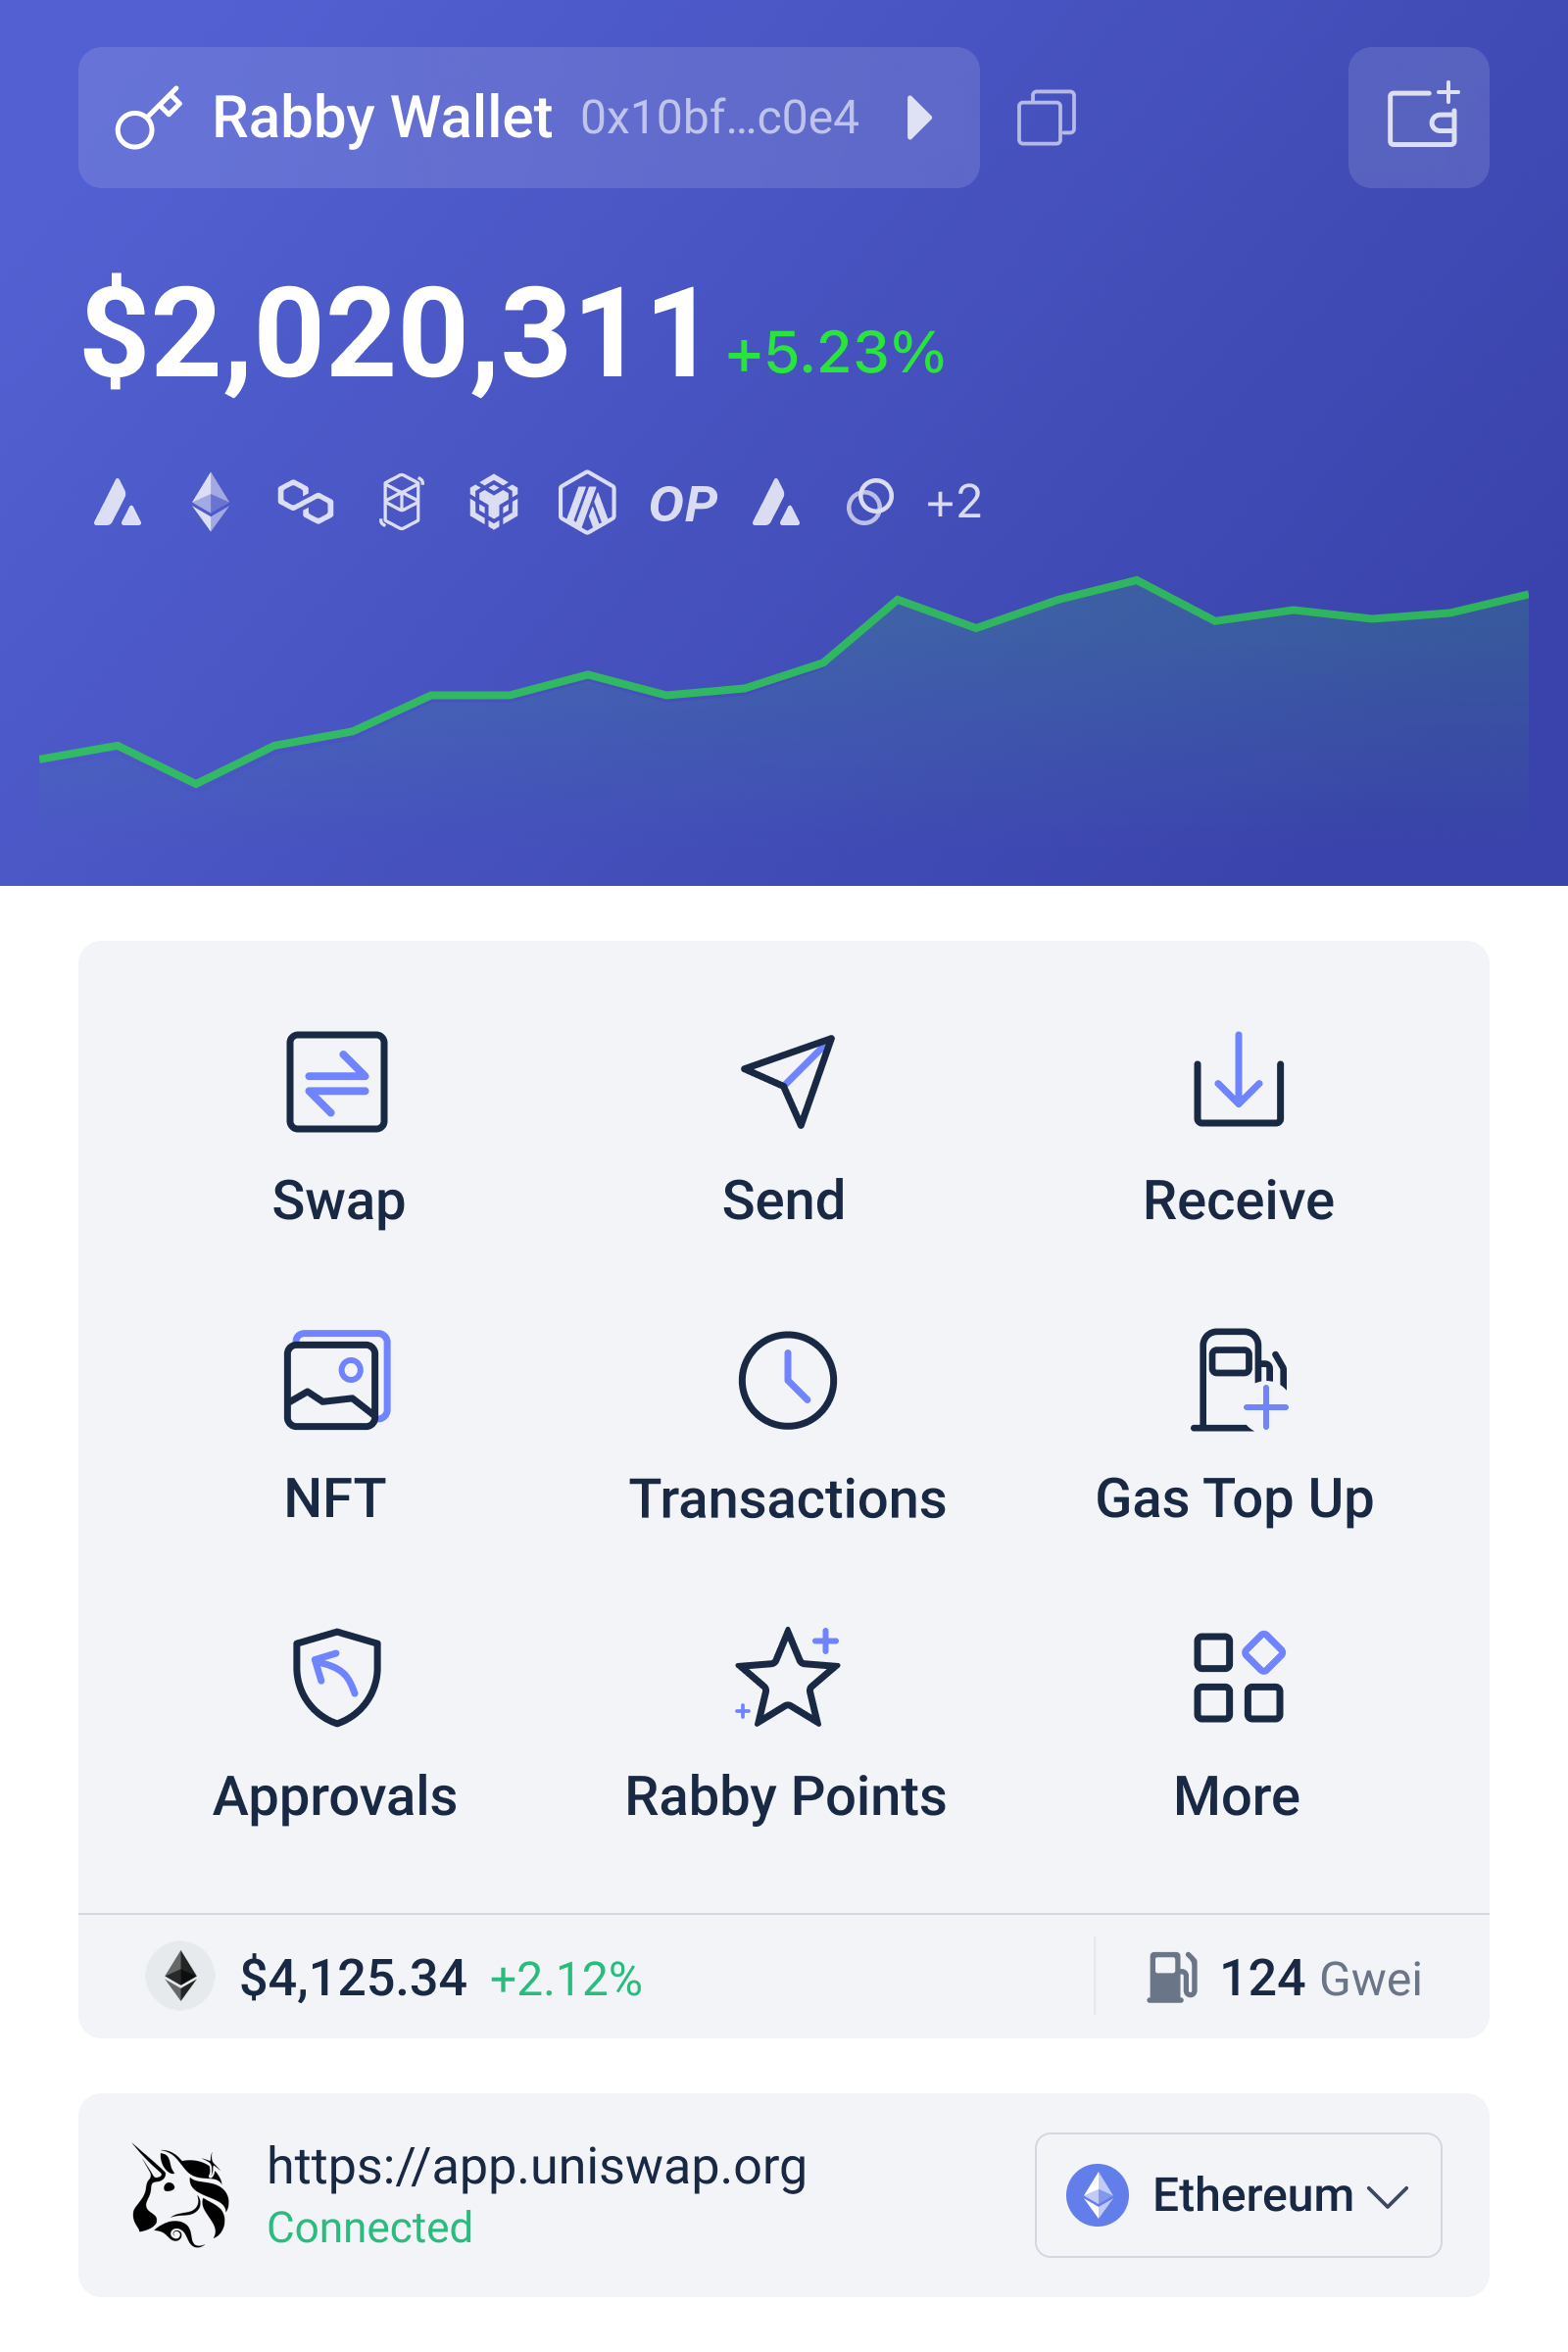
Why transaction simulation changes the wallet decision
A blockchain transaction is not merely a payment instruction. It is a request to execute code under specific conditions. When a user swaps tokens, stakes assets, or deposits into a lending protocol, the transaction may update several balances and permissions at once. A basic wallet can display the destination contract and the amount of native currency used for gas. That information is necessary, but it is often not sufficient for a meaningful risk assessment.
Transaction simulation attempts to show the likely result of execution before the transaction is broadcast. In practical terms, the wallet can estimate which assets will leave the account, which assets may arrive, whether an approval is being granted, and whether a call appears to produce an unexpected result. This creates a more useful mental model: the user is reviewing a proposed state change, not simply clicking “Confirm.” For experienced DeFi users, that distinction can reduce errors caused by confusing contract addresses, stale interfaces, or malicious transaction prompts.
Simulation is still an estimate, not a guarantee. It may depend on the selected network, available RPC data, current block conditions, and the assumptions used by the simulation system. A transaction can behave differently if the market moves, liquidity changes, a protocol’s state updates, or a contract depends on information that is difficult to reproduce off-chain. A successful simulation also does not prove that a protocol is solvent, fairly governed, or free from an exploitable vulnerability. Its value is narrower and more concrete: it can improve visibility into what a particular transaction appears likely to do.
Rabby compared with conventional browser wallets
Rabby and MetaMask-style general-purpose wallets
General-purpose browser wallets have a major advantage: familiarity. They are widely supported, easy to find in wallet-connect menus, and commonly used in tutorials, exchanges, and decentralized applications. That network effect matters. A wallet that works reliably with the applications a user needs may be more useful than a technically sophisticated alternative that creates compatibility friction.
The trade-off is that a conventional signing flow can place more interpretive responsibility on the user. The application may provide one description, while the wallet displays raw or semi-readable contract data. Token approvals can be especially difficult to evaluate because the immediate action may not transfer funds; it grants a contract permission to transfer tokens later. A DeFi-focused wallet that highlights approvals, balance changes, and known risk indicators can make this hidden second step more visible.
Rabby is therefore best understood as a decision-support layer around wallet signing, not as a replacement for blockchain judgment. It may be a strong fit for users who regularly move across Ethereum-compatible networks, compare protocols, or manage several positions. A casual user who makes occasional transfers may value the simplicity and broad familiarity of a general-purpose wallet more than additional analysis. More information is useful only when the user has enough context to interpret it.
Rabby and exchange-hosted wallets
For many people in the United States, a centralized exchange is the first point of entry into crypto. Exchange-hosted balances offer convenience, account recovery processes, and an interface that resembles online banking. They can also simplify fiat deposits and withdrawals. But an exchange account is not the same as self-custody. The user generally relies on the platform to control the underlying keys, process withdrawals, and maintain operational access.
A self-custodial Web3 wallet reverses that arrangement. The user controls the signing credentials and can connect directly to protocols without asking an intermediary to approve every interaction. That autonomy is the central benefit, but it comes with an equally central obligation: a lost recovery phrase, compromised device, or malicious approval can create consequences that customer support may not be able to reverse.
The comparison is not simply convenience versus ideology. It is a difference in failure modes. Exchange users face platform, account, withdrawal, and counterparty risks. Self-custody users face key-management, phishing, approval, and transaction risks. A transaction simulation feature may improve the latter category, but it does not eliminate it. Users should decide which risks they can realistically manage, not assume that self-custody is automatically safer.
Rabby and hardware wallets
Hardware wallets address a different problem. Their primary purpose is to keep signing credentials isolated from an internet-connected computer or phone. Even if a website is compromised, the attacker generally still needs the user to approve a transaction on the hardware device. This separation can materially reduce the impact of some malware and browser attacks.
However, hardware protection does not make a transaction economically or technically sound. A user can still approve a dangerous contract interaction after reading the wrong screen, misunderstanding an allowance, or trusting a fraudulent website. Combining a hardware signer with a wallet interface that provides clearer transaction interpretation can create layered protection: one component protects the key, while another helps the user evaluate the proposed action.
That combination introduces practical friction. Some advanced DeFi flows may require additional confirmations, network configuration, or troubleshooting. Users who trade frequently may be tempted to bypass careful review because signing becomes repetitive. Security controls work only when they remain usable under real conditions, including periods of market stress when speed feels unusually valuable.
The deeper issue: visibility is not the same as safety
One of the most persistent misconceptions in Web3 is that a warning system can determine whether an investment is good. Wallet security tools are generally better at identifying transaction-level concerns than judging financial merit. They may flag an unfamiliar contract, an approval, a suspicious address, or an unexpected asset change. They cannot reliably answer whether a liquidity pool’s yield is sustainable, whether a governance proposal will damage a protocol, or whether a token’s market price reflects reality.
This distinction matters because DeFi risk is layered. There is the risk of signing the wrong action, the risk that the contract contains a bug, the risk that an oracle supplies bad data, the risk that liquidity disappears, and the risk that a protocol’s incentives change. A wallet can improve the first layer and provide clues about some others, but it is not a substitute for contract review, position sizing, or independent research.
Approvals deserve particular attention. An approval is a permission recorded on-chain, often allowing a contract to spend a user’s tokens up to a specified amount. A user may complete a swap successfully and forget that the permission remains active. If the approved contract is later compromised or controlled by an attacker, the standing allowance may become a route to loss. Users should periodically review and reduce permissions where appropriate, especially after interacting with unfamiliar applications. Simulation can make the initial approval easier to notice; it does not automatically manage the permission forever.
A practical framework for choosing among wallets
Rather than ranking wallets on a single security scale, DeFi users can assess them across four questions. First, how much does the wallet explain before signing? Second, how well does it protect the signing key? Third, how broadly does it support the networks and applications the user actually needs? Fourth, how much operational complexity can the user tolerate without developing unsafe shortcuts?
For active DeFi participants, a Rabby-style workflow may fit when transaction interpretation is the main bottleneck. Users who frequently switch networks or interact with less familiar protocols may benefit from seeing likely asset changes before authorizing an action. For users whose highest concern is endpoint compromise or key extraction, a hardware wallet may deserve priority. For beginners who mainly buy, hold, and convert assets, an exchange-hosted account or a simpler wallet may reduce operational mistakes, although it introduces dependence on a centralized provider.
A sensible setup can also be segmented. A user might keep long-term holdings in cold storage, use a separate hot wallet for routine DeFi activity, and maintain a small experimental wallet for new protocols. This does not make losses impossible. It limits the amount exposed to any single approval, device, or application. The principle is similar to compartmentalization in other security systems: reduce the blast radius rather than assuming every barrier will work perfectly.
For users in the US, practical considerations include network fees, tax records, stablecoin exposure, and the distinction between custody and financial advice. A wallet can display transactions, but the user remains responsible for maintaining accurate records of swaps, liquidity actions, staking events, and transfers. The interface may simplify activity; it does not necessarily simplify the underlying tax or accounting treatment. Users should also be cautious when a wallet warning conflicts with an urgent message from a protocol or social-media account. Urgency is frequently a tactic for suppressing review.
What to watch as Web3 wallet design evolves
If wallet interfaces increasingly show simulated outcomes, the likely implication is that signing will become more interpretive and less dependent on raw transaction data. That could improve safety if simulations are accurate, comprehensible, and hard for malicious applications to manipulate. It could also create a new failure mode: users may treat a green indicator as a universal safety certificate. The important signal to watch is not the presence of a feature, but whether the wallet communicates uncertainty and explains what its checks do not cover.
Another open question is how wallets will balance privacy with useful risk analysis. More detailed screening can require more information about addresses, transactions, or application behavior. Users may welcome warnings while remaining uncomfortable with extensive activity profiling. The strongest designs will need to make that trade-off legible rather than hiding it behind a simple security label.
Frequently asked questions
Is Rabby safer than every other Web3 wallet?
No. Its transaction simulation and DeFi-oriented warnings may improve a user’s ability to review proposed actions, but safety also depends on key storage, device security, protocol quality, user behavior, and network conditions. A hardware wallet may offer stronger key isolation, while a simpler wallet may offer better compatibility for a particular application.
Can transaction simulation prevent a DeFi hack?
It can help identify some unexpected transfers, approvals, or contract interactions before signing. It cannot guarantee that a smart contract is secure, that a protocol will remain solvent, or that a market will behave normally. Treat simulation as transaction-level evidence, not as an audit or investment recommendation.
Should advanced users use both a Web3 wallet and a hardware wallet?
Often, that combination is sensible when the wallet interface supports the user’s applications and the hardware device protects long-term signing credentials. The arrangement adds friction, so users should test it with small amounts first and keep separate accounts for different risk levels. The best design is one that users will consistently operate correctly.
The sharpest way to compare Web3 wallets is to ask what kind of uncertainty each one reduces. A general-purpose wallet may reduce onboarding friction. An exchange may reduce key-management demands. A hardware device may reduce exposure of signing credentials. A DeFi-focused wallet may reduce uncertainty about the immediate effects of a transaction. None removes the need for judgment. For serious DeFi users, the most defensible choice is usually not the wallet with the loudest security promise, but the combination of tools that makes risky actions visible, limits potential losses, and remains practical enough to use carefully every time.